World Congress 2025 • Aug 20, 2025 • Session details

Real-World Security for Busy Developers

Kevin Lewis

Stop letting AI expand your attack surface. Discover how to embed continuous security directly into your GitHub workflow to fix vulnerabilities before they reach production.

Pause
Mute Enter Fullscreen
#1 about 4 min

The growing developer responsibility for application security

The shortage of application security specialists and the rise of AI-generated code make vulnerability prevention a core developer responsibility.

#2 about 3 min

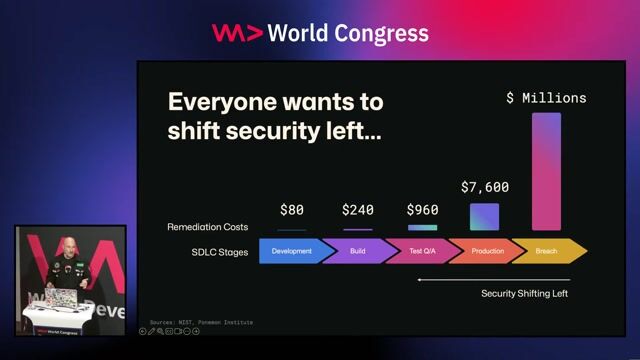
Shifting security left within existing development workflows

Integrating security tooling directly into the early stages of the software development lifecycle prevents costly production data breaches.

#3 about 4 min

Preventing leaked credentials with repository push protection

Proactively blocking commits that contain sensitive credentials prevents the automated exploitation of exposed developer access tokens and keys.

#4 about 3 min

Auditing existing codebases with secret scanning risk assessments

Scanning entire Git histories and generating comprehensive risk assessments helps engineering teams triage and resolve previously leaked internal secrets.

#5 about 5 min

Filtering AI code generations and automating pull request reviews

Utilizing AI coding assistants equipped with vulnerability filtering and pre-commit review capabilities catches architectural risks prior to code submission.

#6 about 5 min

Identifying and resolving vulnerabilities using CodeQL and autofix

Embedding variant analysis engines into pull request checks automatically detects complex code flaws and generates instant remediation code.

#7 about 3 min

Evaluating supply chain risk through automated dependency reviews

Checking new package manifests against global advisory databases during branch merges prevents the introduction of critical software supply chain vulnerabilities.

#8 about 3 min

Automating library updates and vulnerability alerts with Dependabot

Continuous monitoring of project dependency graphs enables automated version upgrades when new transitive library vulnerabilities are publicly disclosed.

#9 about 2 min

Scaling remediation efforts across organizations using security campaigns

Grouping vulnerability management into time-bound automated patching campaigns dramatically increases the volume of resolved flaws across enterprise repositories.

#10 about 2 min

Embedding continuous security practices into standard developer workflows

Unifying automated code scanning, credential protection, and dependency monitoring directly inside version control ecosystems eliminates security-related developer friction.

Matching moments

5:25 min

Shifting left and creating internal security champion programs

Vandana Verma Sehgal · LIVE

2:02 min

Shifting security responsibility into modern developer workflows

Dwayne Mcdaniel · LIVE

1:31 min

Shifting to proactive AI-assisted application defense

Desmond Lamptey Desmond Lamptey · World Congress 2026 North America

3:58 min

Exploring advanced security tooling and community dependency vetting

Niels Tanis Niels Tanis · World Congress 2024

1:00 min

Encouraging broader team adoption of security automation practices

Ramona Schwering Ramona Schwering · World Congress 2024

2:12 min

Deploying automated security analysis tools directly into application pipelines

Ali Yazdani Ali Yazdani · World Congress 2023

Upcoming sessions on this topic

Open session

Supply Chain Security for the Everyday Engineer

  • Pradumna Saraf

    Kestra Technologies

    Quality Assurance Engineer

Open session

Beware of Strangers Bearing Code: Open Source Trust in the Agent Era

  • Vikram Vaswani

    Consultant

Open session

Beyond File Dumps: Context Engineering for Coding Agents

  • Animesh Dutta

    Arm

    Senior Software Engineer

Open session

How is SWE & EM roles are changing in the age of AI

  • Amol Sharma

    Stripe

    Engineering Manager

Open session

Teaching AI Coding Agents to Build It Right the First Time

  • Sajeetharan Sinnathurai

    Microsoft

    Principal Product Manager

Open session

Autopsy of an Autonomous Incident: When the Agent Made It Worse

  • Navin Pai

    StackGen

    Director of Engineering