



LM
Luis Minvielle
Why Upskilling And Reskilling is Important For Developers
over 2 years ago
CoverMyMeds is seeking a Senior Product Security Engineer, AI & DevSecOps to embed security throughout our software development lifecycle, with a focus on AI-enabled products, cloud-native platforms, and DevSecOps practices.
This is a hands-on technical role for a security-minded software developer who understands how applications are designed, written, deployed, and operated. You will partner directly with engineering, platform, architecture, and product teams to translate security requirements into practical guidance, reusable patterns, shared services, and automated controls that help teams deliver products faster and more securely.
The ideal candidate combines hands-on software development experience with deep knowledge of application security, AI security, attack vectors, vulnerability remediation, and security automation. What You’ll Do:
Preferred Skills and Experience:
McKesson complies with all applicable U.S. immigration laws and regulations. The Company does not provide employer support or sponsorship for any immigration related employment benefit for this role.
Applicants must be currently authorized to work in the United States on a fulltime basis without the need for employer support or sponsorship now or in the future. This includes having the legal right to work in the United States without the need for McKesson support or sponsorship for any immigration related employment authorization (e.g., H1B, O1, E3, H1B1, TN, F1 OPT, F1 STEM OPT, F1 CPT, etc.) now or in the future.
We are proud to offer a competitive compensation package at McKesson as part of our Total Rewards. This is determined by several factors, including performance, experience and skills, equity, regular job market evaluations, and geographical markets. The pay range shown below is aligned with McKesson’s pay philosophy, and pay will always be compliant with any applicable regulations. In addition to base pay, other compensation, such as an annual bonus or long-term incentive opportunities may be offered. For more information regarding benefits at McKesson, pleaseclick here.
Our Base Pay Range for this position $140,300 - $233,800
McKesson has become aware of online recruiting-related scams in which individuals who are not affiliated with or authorized by McKesson are using McKesson’s (or affiliated entities, like CoverMyMeds or RxCrossroads) name in fraudulent emails, job postings or social media messages. In light of these scams, please bear the following in mind:
McKesson Talent Advisors will never solicit money or credit card information in connection with a McKesson job application.
McKesson Talent Advisors do not communicate with candidates via online chatrooms or using email accounts such as Gmail or Hotmail. Note that McKesson does rely on a virtual assistant (Gia) for certain recruiting-related communications with candidates.
McKesson job postings are posted on our career site: careers.mckesson.com.
McKesson is an impact-driven, Fortune 10 company that touches virtually every aspect of healthcare. We are known for delivering insights, products, and services that make quality care more accessible and affordable. Here, we focus on the health, happiness, and well-being of you and those we serve - we care.
What you do at McKesson matters. We foster a culture where you can grow, make an impact, and are empowered to bring new ideas. Together, we thrive as we shape the future of health for patients, our communities, and our people. If you want to be part of tomorrow’s health today, we want to hear from you.
This job is hosted externally. Click below to view the full posting and apply.
Talks and stories from around this role — technically off-topic, practically not.
4:58 min
50 sec
 Eileen Uchitelle +1 · Coffee With Developers
3:14 min
6:36 min
1:22 min
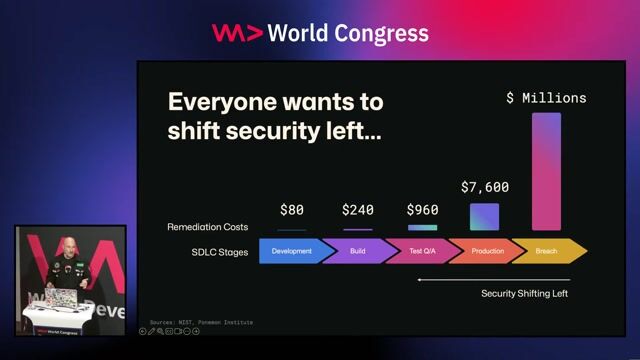
 Joseph Katsioloudes · World Congress 2025
3:30 min
 David Heinemeier Hansson +1 · Coffee With Developers




