WeAreDevelopers LIVE Jan 26, 2022

Stranger Danger: Your Java Attack Surface Just Got Bigger

Vandana Verma Sehgal

Are your open-source Java dependencies secretly hosting malware? Watch live exploit demos of Log4j and learn how shifting security left protects your software supply chain.

Pause
Mute Enter Fullscreen
#1 about 3 min

Setting the stage for software security demos

An overview of upcoming security theory concepts alongside interactive hands-on vulnerability demonstrations.

#2 about 3 min

Upstream supply chain risks in automated technology

How connected devices and software updates introduce potential vectors for network compromise via unprotected upstream sources.

#3 about 3 min

Malware distribution through open source event stream libraries

How attackers inject malicious dependency payloads to compromise the software supply chain through trusted infrastructure.

#4 about 3 min

Identifying command injection flaws in developer infrastructures

Why relying heavily on open source code exposes development environments and staging servers to malicious CI script injections.

#5 about 5 min

Addressing unpatched cross-site scripting vulnerabilities in parsers

The challenges of managing legacy vulnerabilities and delayed security patches within critical open source community projects.

#6 about 3 min

The risk of weak credentials in maintainer accounts

How compromised maintainer credentials and long-standing utility misconfigurations provide root access for widespread supply chain attacks.

#7 about 4 min

Service disruptions from self-sabotaged open source dependencies

The severe operational impact when vital open source maintainers intentionally remove or corrupt central ecosystem packages.

#8 about 8 min

Analyzing the global impact of the Log4j vulnerability

How exploiting unvalidated log file inputs allows attackers to achieve unauthorized control over critical server operations.

#9 about 13 min

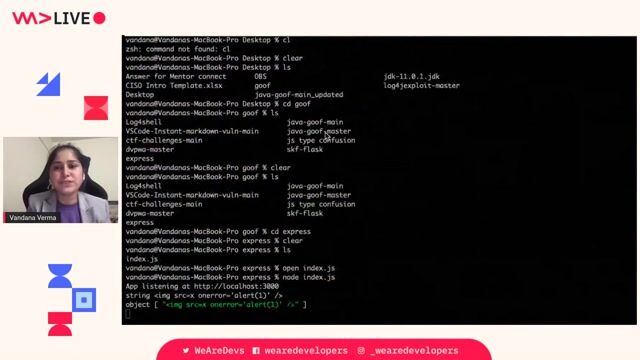
Bypassing input sanitization using javascript type confusion

A framework demonstration revealing how submitting parameter arrays instead of strings bypasses typical cross-site scripting sanitization checks.

#10 about 12 min

Exposing remote code execution via unpatched Java utilities

Simulating a known vulnerability using a flawed Apache Struts implementation to upload untrusted payloads onto enterprise systems.

#11 about 31 min

Simulating the Log4Shell zero-day exploit in local terminals

A practical walkthrough for cloning, building, and triggering the Log4j command injection using Maven and a vulnerable JDK runtime.

#12 about 6 min

Shifting left and creating internal security champion programs

Strategies for integrating robust security scanning directly into agile continuous integration pipelines through cross-functional developer advocacy.

#13 about 4 min

Automating vulnerability detection across diverse development ecosystems

Utilizing automated analysis tools to discover and patch flaws in open source components and container registries inside standard IDEs.

#14 about 27 min

Exploring pathways to application security careers and research workflows

Exploring paths into application security roles, vulnerability disclosure etiquette, and the necessity of developer-led organizational security.

Matching moments

2:00 min

Mitigating risks from supply chain attacks and vulnerable libraries

Jasmin Azemović Jasmin Azemović · World Congress 2023

2:46 min

Mapping the complete software supply chain attack surface

Matthew Brady Matthew Brady · World Congress 2026 Europe

2:13 min

Understanding software vulnerabilities and prominent exploits

Mohammad-Ali A'râbi Mohammad-Ali A'râbi · World Congress 2026 Europe

3:39 min

Exploring the mechanics of software supply chain attacks

Chris Heilmann +2 · LIVE

3:59 min

Vulnerabilities within the cyber software supply chain

Jon Geater · World Congress 2023

1:19 min

Real-world impact of remote code execution vulnerabilities

Alexander Pirker · World Congress 2022

Upcoming sessions on this topic

Open session

World Congress 2026 North America

September 24, 2026 · 14:10–14:40

Stage 2

Know Your Enemies: Live Exploit of a PHP Engine Security Breach

Alexandre Daubois

CTO of Les-Tilleuls.coop / Symfony Core Team / PHP & FrankenPHP Core Maintainer

Alexandre Daubois
Open session

World Congress 2026 North America

September 24, 2026 · 11:40–12:10

Stage 3

Stop Running Mystery Meat in Production

Jeroen van Erp

Technical Advocate @ SUSE

Jeroen van Erp
Open session

World Congress 2026 North America

September 25, 2026 · 13:30–14:00

Stage 9

On the Public Clock: Open-Source Defense When You're Not in the Club

Nicholas Muy

VP Engineering Platform and Security at Scrut.io

Nicholas Muy
Open session

World Congress 2026 North America

September 25, 2026 · 15:00–17:00

Stage 12

Secure development from pull request to production with GitHub

Sam Jarvinen

Senior Solutions Engineer, GitHub
Sam Jarvinen
Open session

World Congress 2026 North America

September 23, 2026 · 14:00–14:30

Stage 1

Supply Chain Security When Agents Write the Code

Ajeet Raina

Developer Advocate, Docker

Ajeet Raina
Open session

World Congress 2026 North America

September 25, 2026 · 09:40–10:10

Stage 4

Your registry can't stop a valid login. What happens then?

Khushboo Verma

Systems Engineer at Cloudflare
Khushboo Verma