WeAreDevelopers LIVE Apr 18, 2023

Securing Secrets in the GitOps era

Alex Soto

Standard Kubernetes secrets are merely Base64-encoded, leaving your repositories exposed. Ready to build an onion-layered defense and completely eliminate hardcoded credentials from your cloud-native architecture?

Pause
Mute Enter Fullscreen
#1 about 7 min

Introduction to securing secrets in GitOps deployments

Secrets require multiple layers of protection to remain concealed within deployment environments.

#2 about 5 min

Understanding continuous delivery in the GitOps model

Git serves as the single source of truth for both application and infrastructure code.

#3 about 3 min

Application delivery workflow with continuous integration repositories

Application code changes trigger an automated pipeline that updates infrastructure configurations.

#4 about 3 min

Automating cluster synchronization with Argo CD controllers

Argo CD monitors configuration repositories and applies infrastructure changes to Kubernetes clusters.

#5 about 3 min

Vulnerabilities of storing unencrypted secrets in repositories

Base64 encoding fails to securely protect sensitive information inside Kubernetes secret files.

#6 about 3 min

Encrypting secret manifests using the Sealed Secrets project

Sealed Secrets introduces public and private key pairs to encrypt sensitive data before repository storage.

#7 about 4 min

Generating and applying sealed secret manifests via Kubeseal

Kubeseal encrypts standard secrets into safely distributable forms that controllers decrypt inside the cluster.

#8 about 5 min

Vulnerabilities of plaintext secrets within the etcd database

Cluster administrators or attackers can retrieve unencrypted secrets by accessing etcd logs or backups.

#9 about 2 min

Protecting etcd databases using Key Management System plugins

Key Management Systems delegate encryption tasks to external providers like HashiCorp Vault to secure data at rest.

#10 about 6 min

Demonstrating database encryption at rest with HashiCorp Vault

Integrating a Vault instance guarantees that etcd database queries cannot extract unencrypted operational data.

#11 about 3 min

Injecting secrets directly into pod memory structures

Avoiding environment variables and disk files blocks localized attackers from recovering application credentials.

#12 about 3 min

Generating dynamic application secrets using HashiCorp Vault engines

Dynamic secrets automatically generate temporary access credentials without requiring localized storage or human interaction.

#13 about 5 min

Retrieving dynamic database credentials during pod runtime

Deploying a frontend application that securely fetches generated credentials directly from a dynamic storage engine.

#14 about 3 min

Additional resources on GitOps and Kubernetes secret management

Authors and open-source materials offer deeper architectural insights and practical configuration recipes.

#15 about 3 min

Transitioning toward developer responsibility in security models

Modern enterprises increasingly require developers to understand and enforce infrastructure security constraints.

#16 about 2 min

Evaluating decentralized versus centralized secret management strategies

Organizational maturity requirements dictate whether secrets should be centrally controlled or managed by individual capability teams.

#17 about 2 min

Synchronizing localized environments using service virtualization

Containerized profiles and mocked services isolate application access without loading complex developer environments.

#18 about 2 min

Converting dynamic repository secrets into localized environment files

Agent utilities parse external secret providers into local environment variables for application consumption.

#19 about 2 min

Defining developer experience functions within modern engineering teams

Managing the usability of internal tooling improves adoption speeds and minimizes configuration friction for coding teams.

Matching moments

3:09 min

Injecting sensitive configuration values via Kubernetes secrets

Hannes Norbert Göring · LIVE

4:08 min

Security risks of storing native Kubernetes secrets in git

Davide Imola Davide Imola · LIVE

2:30 min

Handling passwords and certificates securely via Kubernetes secrets

Aurélie Vache Aurélie Vache · World Congress 2026 Europe

1:53 min

Transitioning toward DevSecOps with dynamic scanning and secrets management

Christoph Ruggenthaler · LIVE

5:03 min

Designing a self-service internal developer platform with GitOps

Patrick Koss Patrick Koss · World Congress 2026 Europe

3:42 min

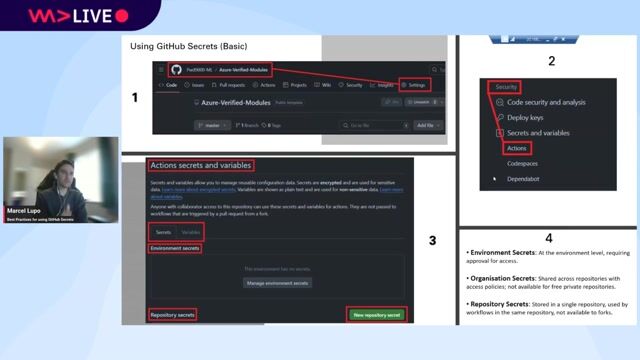
Best practices for ignoring and securely vaulting secrets

Dwayne Mcdaniel · LIVE

Upcoming sessions on this topic

Open session

World Congress 2026 North America

September 25, 2026 · 15:00–17:00

Stage 12

Secure development from pull request to production with GitHub

Sam Jarvinen

Senior Solutions Engineer, GitHub
Sam Jarvinen
Open session

World Congress 2026 North America

September 23, 2026 · 15:45–17:45

Stage 10

Securing the Agentic Stack: Docker Hardened Images and Supply Chain Security

Ajeet Raina

Developer Advocate at Docker
Ajeet Raina
Open session

World Congress 2026 North America

September 25, 2026 · 12:30–14:30

Stage 11

Docker sandboxes: protect your secrets, tokens, and personal data from AI agent mistakes

Kristiyan Velkov

Front-End Advocate | Speaker | AI & DevOps | Docker Captain | Cursor Ambassador | DevReal | Tech Blogger | Book Author
Kristiyan Velkov
Open session

World Congress 2026 North America

September 24, 2026 · 11:40–12:10

Stage 3

Stop Running Mystery Meat in Production

Jeroen van Erp

Technical Advocate @ SUSE

Jeroen van Erp
Open session

World Congress 2026 North America

September 23, 2026 · 14:00–14:30

Stage 1

Supply Chain Security When Agents Write the Code

Ajeet Raina

Developer Advocate, Docker

Ajeet Raina
Open session

World Congress 2026 North America

September 24, 2026 · 14:50–15:20

Tech Leaders Stage

Ship with Context: GitLab Orbit and Google Cloud for AI-Powered Software Delivery

Michael Angelo Rivera, Mike Duchesne

Michael Angelo Rivera
Mike Duchesne