
Cyber & Information Security Manager
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
Prepare application
- Draft this with your agent
- Open in Claude
- Open in ChatGPT
Role details
Tech stack
Job description
We’re looking for an experienced Cyber & Information Security Manager to join a leading organisation based in Teesside, working on a hybrid basis with 1-2 days per week on site.
This is a key leadership role responsible for developing and enhancing cyber security, information security, data privacy and compliance programmes, helping protect critical digital assets and systems.
You’ll lead on cyber risk, incident response, regulatory compliance, audits, security frameworks and continuous improvement, while managing and developing an Information Security team.
Requirements
- Proven experience leading cyber/information security and compliance teams
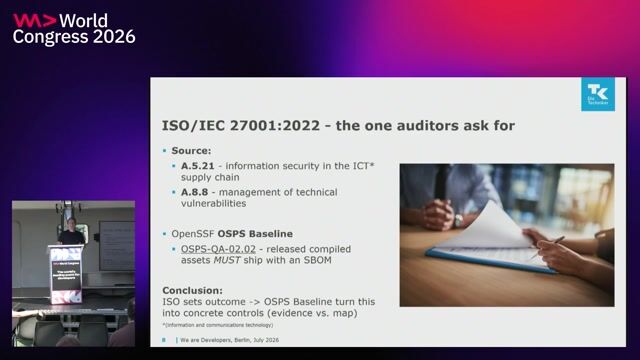
- Strong knowledge of NIST, NIS2, ISO 27002, Cyber Essentials Plus and GDPR
- Experience managing enterprise risk registers and security metrics
- Experience with ISO 27002/Cyber Essentials Plus audits and ISMS development
- Strong stakeholder management and leadership skills
- CISSP, CISM, CISA or similar certification highly desirable
Apply for this position
This job is hosted externally. Click below to view the full posting and apply.
Prepare application
- Draft this with your agent
- Open in Claude
- Open in ChatGPT
Good distractions
Talks and stories from around this role — technically off-topic, practically not.
Moments
Explore playlistsVideos
See allRelated articles
See all
Events like RSAC Get You CISOs. Developers Decide What Actually Gets Deployed.
Best Companies to work for in London: Top 25 Companies in 2023
How We Built a Worry-Free System That Runs for 10+ Years – And What We’d Do Again
From developer to manager – what does it take to become an engineering manager?