World Congress 2026 Europe Jul 9, 2026 Session details

One Pipeline, Three Regulator - SBOM Compliance for the Developer

Marcus Ross

Turn complex regulations like the EU Cyber Resilience Act into a natural byproduct of your pipeline. Automate SBOM compliance and vulnerability scanning without drowning in paperwork.

Pause
Mute Enter Fullscreen
#1 about 7 min

Legal frameworks mandating software bill of materials

European regulations like the Cyber Resilience Act require product teams to build transparency by tracking software components.

#2 about 3 min

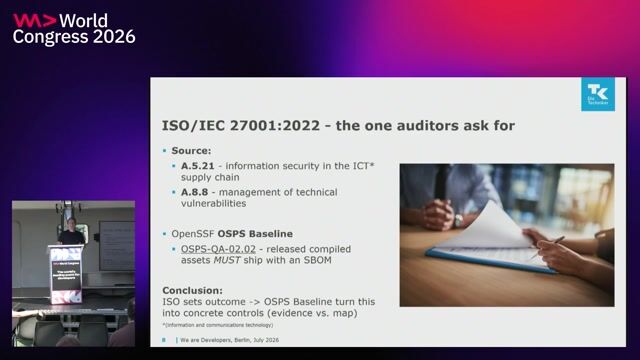
Satisfying ISO 27001 supply chain and vulnerability requirements

Using a software bill of materials acts as an inventory to provide technical evidence for ISO 27001 audits.

#3 about 3 min

Securing code provenance with digital identity signatures

Cryptographically tying developer identity to code commits secures code systems against spoofing and establishes verifiable provenance.

#4 about 2 min

Implementing keyless commit signing with Sigstore gitsign

Configuring version control with ephemeral certificates simplifies developer onboarding by signing code without long-lived keys.

#5 about 3 min

Distinguishing between basic sign-offs and cryptographic signatures

Recognizing the distinction between simple text sign-offs and cryptographic signatures prevents unverified release artifacts.

#6 about 3 min

Resolving the SPDX and CycloneDX format dilemma

Using open-source tools to flawlessly convert between formats eliminates friction inside continuous integration pipelines.

#7 about 3 min

Navigating the CVE data crisis and fragmented vulnerability streams

Consolidating multiple package ecosystem feeds counters the data crisis caused by slowdowns at the National Vulnerability Database.

#8 about 3 min

Scanning software distributions with the OpenSSF OSV schema

Leveraging the OSV-Scanner allows offline, version-accurate vulnerability matching directly against a software bill of materials.

#9 about 3 min

Collaborating on risk appetite and CVE remediation strategies

Facilitating discussions between engineering and security operations establishes realistic vulnerability remediation expectations instead of aiming for zero.

#10 about 2 min

Unifying software compliance into standard delivery pipelines

Embedding code provenance and bill of materials generation directly into deployment commands turns compliance into a natural byproduct.

Matching moments

2:46 min

Mapping the complete software supply chain attack surface

Matthew Brady Matthew Brady · World Congress 2026 Europe

4:55 min

Automating compliance checks into delivery pipelines

Antoine Thomas Antoine Thomas · Europe 2026 Virtual

3:07 min

Navigating software integration compliance in safety automotive environments

Nico Schmidt · LIVE

3:58 min

Exploring advanced security tooling and community dependency vetting

Niels Tanis Niels Tanis · World Congress 2024

2:46 min

Adopting actionable frameworks for software bills of materials

Vandana Verma · LIVE

2:06 min

Why automated compliance matters for developers

Uwe Korn Uwe Korn · World Congress 2026 Europe

Upcoming sessions on this topic

Open session

World Congress 2026 North America

September 23, 2026 · 14:00–14:30

Stage 1

Supply Chain Security When Agents Write the Code

Ajeet Raina

Developer Advocate, Docker

Ajeet Raina
Open session

World Congress 2026 North America

September 25, 2026 · 13:30–14:00

Stage 9

On the Public Clock: Open-Source Defense When You're Not in the Club

Nicholas Muy

VP Engineering Platform and Security at Scrut.io

Nicholas Muy
Open session

World Congress 2026 North America

September 24, 2026 · 11:40–12:10

Stage 3

Stop Running Mystery Meat in Production

Jeroen van Erp

Technical Advocate @ SUSE

Jeroen van Erp
Open session

World Congress 2026 North America

September 25, 2026 · 15:00–17:00

Stage 12

Secure development from pull request to production with GitHub

Sam Jarvinen

Senior Solutions Engineer, GitHub
Sam Jarvinen
Open session

World Congress 2026 North America

September 23, 2026 · 15:45–17:45

Stage 10

Securing the Agentic Stack: Docker Hardened Images and Supply Chain Security

Ajeet Raina

Developer Advocate at Docker
Ajeet Raina
Open session

World Congress 2026 North America

September 24, 2026 · 12:15–12:45

Stage 6

AI vs. AI: Defending the open source supply chain with agentic workflows

Manfred Moser

Senior Principal DevRel Engineer at Chainguard
Manfred Moser