

LM
Luis Minvielle
How to Become an AI Engineer
almost 3 years ago
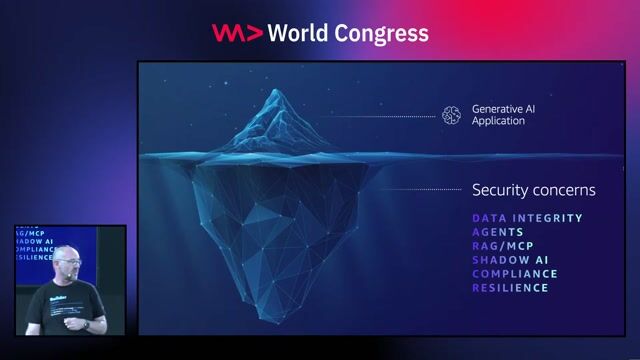
Organisations are rolling out AI faster than they can secure it. LLM integrations, internal copilots and agents that can call APIs are going live, and the security teams responsible for them are still working out what “good” looks like. This role sits right in that gap.
I’m working with a major UK consultancy to find an AI Security Consultant. You’ll be a Cyber Security Consultant first, with a focus on how to secure the use of AI in organisations.
Day to day, that means advising clients on core security across cloud, identity, applications, data and governance, while also helping them get to grips with the new risks AI brings in. Think prompt injection, excessive agency, data leakage, insecure tool use and weak human oversight.
What you’ll be doing
You’ll run security assessments and architecture reviews, then turn the findings into clear, prioritised advice that makes sense to both engineers and senior stakeholders. On the AI side, you’ll threat model agentic workflows, review LLM-based applications, and help clients put sensible guardrails in place around permissions, sandboxing, logging and human-in-the-loop controls. You’ll also help them set up governance and assurance for AI systems, from early experimentation through to production.
You’ll help security teams use AI safely in their own operations, whether that’s alert triage, threat intel enrichment, incident summarisation, detection engineering or vulnerability prioritisation.
Nice to have: experience with AI governance or model risk, familiarity with NIST AI RMF, OWASP LLM and Agentic guidance, MITRE ATLAS, ISO 27001 or NIST CSF, hands-on SOC/SIEM/SOAR exposure, and certifications like CISSP, CISM, CCSP or GIAC., * Cybersecurity
This job is hosted externally. Click below to view the full posting and apply.
Talks and stories from around this role — technically off-topic, practically not.
2:37 min
 Mike · World Congress 2025
1:10 min
 Dennis Schulz +1 · World Congress 2026 Europe
1:20 min
2:14 min
1:56 min
3:00 min
 Deepu · World Congress 2025



