


BB
Benedikt Bischof
From Build to Breach: Hacking Kubernetes Through the Supply Chain
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
How does a seemingly harmless NPM package bypass your Kubernetes firewalls? Watch a realistic supply chain attack exploit AI-generated code and DNS tunneling to stealthily extract cluster secrets.
Matching moments
1:39 min
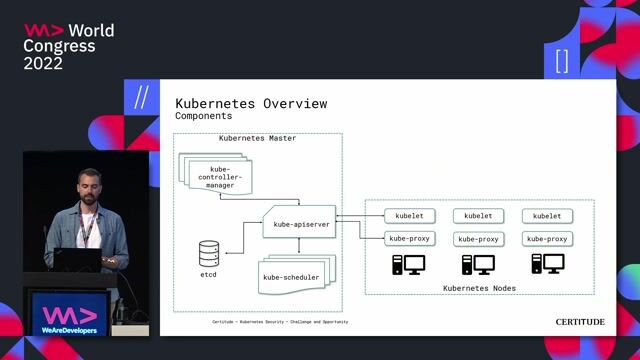
Introduction to Kubernetes security challenges and opportunities
Marc Nimmerrichter · World Congress 2022
3:36 min
Understanding software supply chain threats and security risks
 Andrei Epure · World Congress 2024
3:39 min
Exploring the mechanics of software supply chain attacks
 Chris Heilmann +2 · LIVE
1:03 min
Highlighting supply chain vulnerabilities from obfuscated package manager backdoors
Daniel Cranney +1 · LIVE
4:40 min
Assessing common Kubernetes security incidents and misconfigurations
 Rico Komenda · World Congress 2025
5:13 min
Identifying sophisticated supply chain attacks and simulated software vulnerabilities
Mohamed Shiralizadeh · Coffee With Developers
More from World Congress 2026 Europe
Related videos
Related articles

DC
Daniel Cranney

CH
Chris Heilmann

From learning to earning
Jobs that call for the skills explored in this talk.
27 days ago
•
Verified
Senior Supply Chain Security Engineer

Docker, Inc.
Expert
Remote
Linux
Kubernetes
27 days ago
•
Verified
Principal Software Engineer, Docker Hardened Images
Docker, Inc.
Expert
Remote
Kubernetes
27 days ago
•
Verified
Senior Principal Software Engineer, Docker and Ecosystem
Docker, Inc.
Seattle, United States
Expert
Remote
Cloud (AWS/Google/Azure)
27 days ago
•
Verified
Senior Software Engineer, Secure Build
Docker, Inc.
Expert
Remote
Go
12 days ago
Cloud Engineer (German)

Stackit
Barcelona, Spain
Git
Okta
OAuth
21 days ago
Principal Solutions Architect, Professional Services
Docker, Inc.
A Coruña, Spain
€119k–170k
Okta
Docker
OpenID