World Congress 2022 β€’ Jun 15, 2022

Hacking Kubernetes: Live Demo Marathon

Andrew Martin

How fast can a single npm dependency compromise your Kubernetes cluster? Watch this live demonstration break container isolation to prove why active intrusion tripwires are your only failsafe.

Pause
Mute Enter Fullscreen
#1 about 5 min

Mapping the attack surface of a Kubernetes cluster

Starting a penetration test requires understanding how Linux container namespaces and orchestrator abstractions interact.

#2 about 7 min

Threat modeling techniques for cloud native infrastructure

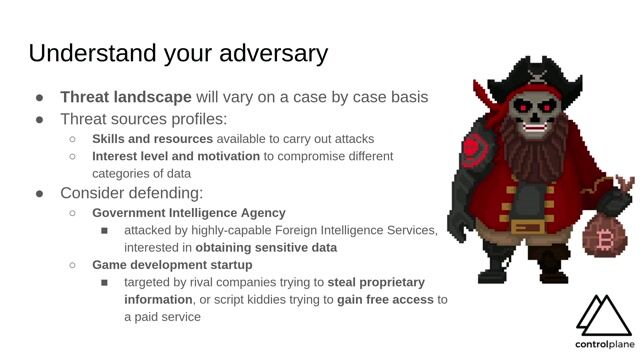
Modeling adversaries from script kiddies to organized crime helps build proportionate and cost-effective security controls.

#3 about 7 min

Executing a software supply chain attack with dependencies

Abusing execution hooks in package managers allows attackers to steal context and establish reverse shells.

#4 about 9 min

Breaking out of overprivileged pods using host mapping

Misconfigured security policies that share the host process ID space allow attackers to manipulate root namespaces.

#5 about 10 min

Escaping unprivileged containers using the Dirty Pipe exploit

Overwriting out-of-bounds executable memory via execution symlinks allows an attacker to gain a root shell directly on the underlying host node.

#6 about 9 min

Pivoting from a compromised kubelet to cloud accounts

Enumerating orchestrator-injected secrets mapped on host volumes reveals credentials that can escalate privileges into wider cloud environments.

#7 about 3 min

Discussing container privilege escalation and volume security risks

Audience questions clarify the limits of rootless containers and highlight security risks introduced by shared volume mounts.

Matching moments

5:59 min

Live demonstration of vulnerability exploitation and zero trust mitigation

Jan Peer StΓΆcklmair Jan Peer StΓΆcklmair Β· World Congress 2026 Europe

4:40 min

Assessing common Kubernetes security incidents and misconfigurations

Rico Komenda Rico Komenda Β· World Congress 2025

1:39 min

Introduction to Kubernetes security challenges and opportunities

Marc Nimmerrichter Β· World Congress 2022

5:28 min

Executing a DNS exfiltration attack in Kubernetes

Ali Alp Ali Alp Β· World Congress 2026 Europe

4:27 min

Identifying software vulnerabilities and typical configuration weaknesses

Marc Nimmerrichter Β· World Congress 2022

5:44 min

Demonstrating a container escape using kernel vulnerabilities

Marc Nimmerrichter Β· World Congress 2022

Upcoming sessions on this topic

Open session

World Congress 2026 North America

September 25, 2026 Β· 09:40–10:10

Stage 4

Your registry can't stop a valid login. What happens then?

Khushboo Verma

Systems Engineer at Cloudflare
Khushboo Verma
Open session

World Congress 2026 North America

September 24, 2026 Β· 11:40–12:10

Stage 3

Stop Running Mystery Meat in Production

Jeroen van Erp

Technical Advocate @ SUSE

Jeroen van Erp
Open session

World Congress 2026 North America

September 25, 2026 Β· 15:30–16:00

Mainstage

One Boundary for the Agentic Era

Mark Lechner

Chief Information Security Officer of Docker
Mark Lechner
Open session

World Congress 2026 North America

September 25, 2026 Β· 10:20–10:50

Stage 4

rm -rf: Horror Stories From Unsandboxed AI Agents (and How Docker Fixes This)

Rishab Kumar

Staff Developer Evangelist @ Twilio

Rishab Kumar
Open session

World Congress 2026 North America

September 25, 2026 Β· 12:30–14:30

Stage 13

Docker sandboxes: protect your secrets, tokens, and personal data from AI agent mistakes

Kristiyan Velkov

Front-End Advocate | Speaker | AI & DevOps | Docker Captain | Cursor Ambassador | DevReal | Tech Blogger | Book Author
Kristiyan Velkov
Open session

World Congress 2026 North America

September 24, 2026 Β· 14:10–14:40

Stage 2

Know Your Enemies: Live Exploit of a PHP Engine Security Breach

Alexandre Daubois

CTO of Les-Tilleuls.coop / Symfony Core Team / PHP & FrankenPHP Core Maintainer

Alexandre Daubois