
DC
Daniel Cranney
Bullet-Proof APIs: The OWASP API Security Top Ten
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
Are your APIs bleeding data through mass assignment or faulty authorization? Master the OWASP Top Ten to embed bullet-proof defense mechanisms directly into your architecture.
Matching moments
6:11 min
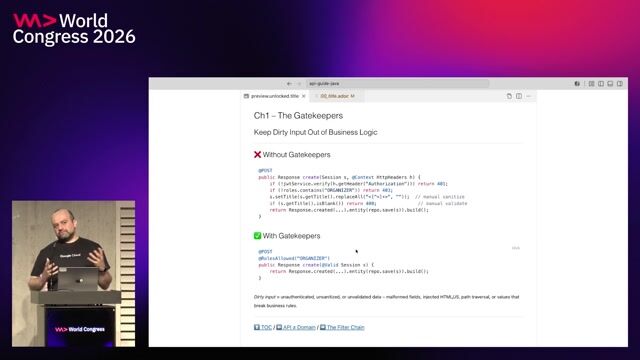
Overview of the 2025 OWASP Top Ten list
 Christian Wenz · World Congress 2026 Europe
12:11 min
Identifying and mitigating top software vulnerability classes
Thomas Konrad · World Congress 2021
3:15 min
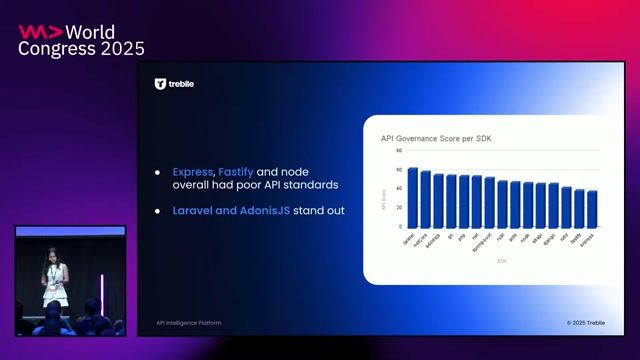
The current state of enterprise APIs and security trends
 Pratim Bhosale · World Congress 2025
41 sec
Identifying missing security risks beyond the top ten
Christian Wenz · World Congress 2026 Europe
2:00 min
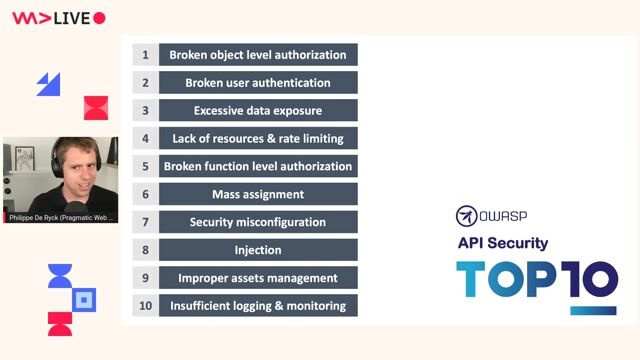
Key architectural takeaways for building secure APIs
Philippe De Ryck · LIVE
1:08 min
Overview of the OWASP MCP top ten vulnerabilities
 Jose Manuel Ortega · Europe 2026 Virtual
More from World Congress 2025
Related videos
Related articles

HS
Harman Singh

BB
Benedikt Bischof

DC
Daniel Cranney

From learning to earning
Jobs that call for the skills explored in this talk.
about 2 months ago
Staff Developer Advocate, GitHub Security Lab

GitHub
United States
Experienced
$121k–323k
Remote
Git
Github
Databases
2 months ago
Forward Deployed Software Engineering - Senior Manager
PwC
San Francisco, CA, United States
Expert
$124k–335k
Code Review
Api Management
Software Systems
2 months ago
Forward Deployed Software Engineering - Manager
PwC
San Francisco, CA, United States
Experienced
$99k–266k
Microservices
Api Management
Software Systems
27 days ago
•
Verified
Senior Principal Software Engineer, Docker and Ecosystem

Docker, Inc.
Seattle, United States
Expert
Remote
Cloud (AWS/Google/Azure)
2 months ago
P&C Technical Solutions Architect, Manager
PwC
San Diego, CA, United States
Expert
$99k–232k
Togaf
Data Streaming
Data Analytics
3 months ago
Staff Engineer, Security Engineering Partners

Twilio
United States
Expert
Remote
Twilio
Cloud Computing
Containerization