

DC
Daniel Cranney
From Shadow AI to Secure Intelligence: Safe AI Usage in the Enterprise
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
Is shadow AI quietly exposing your sensitive enterprise data through innocent-looking prompts? Learn how to implement a dynamic control plane to secure complex agentic workflows.
Matching moments
3:33 min
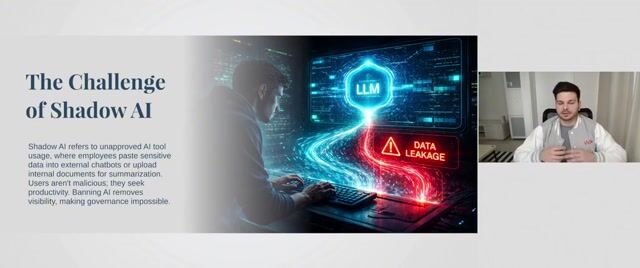
Managing shadow ai adoption and enterprise data leakage
 Kai Grunwitz +2 · World Congress 2025
2:43 min
Setting effective guardrails for enterprise agentic AI adoption
 Julia Kordick · Coffee With Developers
2:42 min
Managing the spread and security risks of shadow AI
 Maish Saidel-Keesing · World Congress 2025
3:08 min
Understanding the landscape of AI capabilities and risks
Balázs Kiss · World Congress 2023
4:15 min
Security integration and AI skepticism in developer tooling
 Chris Heilmann +2 · LIVE
44 sec
Addressing corporate compliance challenges with secure enterprise AI
 Hissan Usmani · World Congress 2025
More from World Congress 2026 Europe - Virtual Stage
Related videos
Related articles

DC
Daniel Cranney
CH
Chris Heilmann

CH
Chris Heilmann
From learning to earning
Jobs that call for the skills explored in this talk.
about 1 month ago
•
Verified
Partner Sales Director - AI Alliances - Model Providers

Dynatrace
San Francisco, United States
Expert
Remote
DevOps
AI Frameworks
Machine Learning
18 days ago
Senior AI Developer
PwC
United States
Expert
Remote
Docker
Github
Fastapi
2 days ago
•
Verified
AI Software Engineer (Germany)
Sunhat
Berlin, Germany
Expert
€70k–100k
Remote
REST
TypeScript
AI Frameworks
16 days ago
Director - AI-enabled Transformation in the Insurance Sector
PwC
London, UK
Generative AI
Cloud Computing
Artificial Intelligence
about 1 month ago
•
Verified
Senior AI/ML Engineer
PagerDuty
Lisbon, Portugal
Expert
Remote
AI Frameworks
AI-assisted coding tools
20 days ago
•
Verified
Head of Agentic AI / Lead AI Engineer
1st solution consulting gmbh
Barcelona, Spain
Expert
€70k–80k
Python
OpenAI API
AI Frameworks