


BB
Benedikt Bischof
JavaScript Congress
•
Nov 24, 2021
Vulnerable VS Code extensions are now at your front door
Raul Onitza-Klugman , Kirill Efimov
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
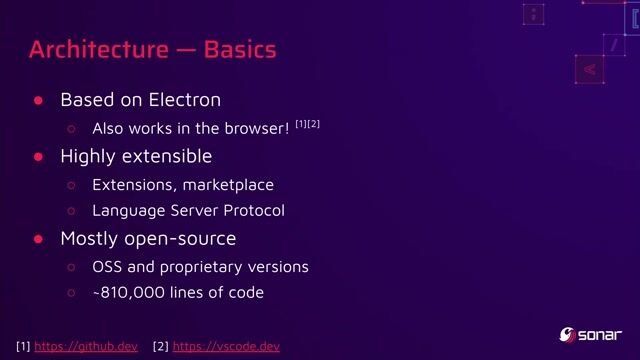
Security researchers analyzed the VS Code marketplace. Their findings are alarming. Discover how attackers weaponize popular extensions to steal SSH keys and execute remote code on developer machines.
Matching moments
5:44 min
Risks of malicious VS Code extensions and AI assistants
 Chris Heilmann +3 · LIVE
4:53 min
Introduction to VS Code security risks and threat models
Thomas Chauchefoin +1 · World Congress 2023
2:17 min
Security incidents in extension marketplaces and package managers
Chris Heilmann +2 · LIVE
5:26 min
Exploiting path traversal vulnerabilities in code editor extensions
Sonya Moisset · World Congress 2023
2:14 min
Exploiting exposed network services in developer IDE extensions
Thomas Chauchefoin +1 · World Congress 2023
49 sec
Targeting developer integrated development environments and plugins
Vandana Verma · LIVE
More from JavaScript Congress
Related videos
Related articles

DC
Daniel Cranney

DC
Daniel Cranney

DC
Daniel Cranney

From learning to earning
Jobs that call for the skills explored in this talk.
about 2 months ago
Staff Developer Advocate, GitHub Security Lab
GitHub
United States
Experienced
$121k–323k
Remote
Git
Github
Databases
about 1 month ago
•
Verified
Senior Supply Chain Security Engineer
Docker, Inc.
Expert
Remote
Linux
Kubernetes
6 days ago
Penetration Tester / Red team Specialist

Raiffeisen Bank International AG
Stans, Austria
€47k
Linux
OAuth
Scripting
28 days ago
•
Verified
SoC Offensive Security Staff Engineer

Arm
Austin, United States
Experienced
$198k–268k
Remote
Network Security
about 1 month ago
•
Verified
Senior Principal Software Engineer, Docker and Ecosystem
Docker, Inc.
Seattle, United States
Expert
Remote
Cloud (AWS/Google/Azure)
3 months ago
Staff Engineer, Security Engineering Partners

Twilio
United States
Expert
Remote
Twilio
Cloud Computing
Containerization