


BB
Benedikt Bischof
WeAreDevelopers LIVE
•
Apr 20, 2022
The attacker's footprint
Antonio De Mello , Amine Abed
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
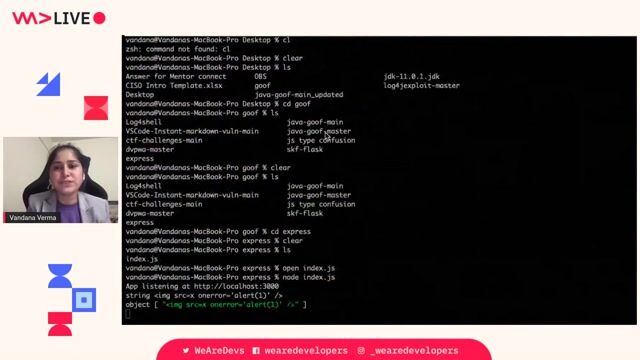
Could you trace an attacker's exact steps after a breach? Watch a live attack simulation and learn to reconstruct the timeline using manual log analysis.
Matching moments
51 sec
Exploring offensive security with red team tooling
Stefania Chaplin · World Congress 2022
1:15 min
Retaining the defender advantage in the cybersecurity race
 Michele Zuccala +4 · World Congress 2026 Europe
4:48 min
Using intentionally vulnerable applications for practical security training
 Bozidar Spirovski +1 · Coffee With Developers
4:05 min
Demonstrating automated defense strategies at prominent cybersecurity conferences
Ben Hopkins +1 · Coffee With Developers
2:41 min
Setting the stage for software security demos
Vandana Verma Sehgal · LIVE
26:47 min
Exploring pathways to application security careers and research workflows
Vandana Verma Sehgal · LIVE
More from WeAreDevelopers LIVE
Related videos
Related articles

DC
Daniel Cranney

CH
Chris Heilmann

CH
Chris Heilmann

From learning to earning
Jobs that call for the skills explored in this talk.
28 days ago
•
Verified
SoC Offensive Security Staff Engineer

Arm
Austin, United States
Experienced
$198k–268k
Remote
Network Security
6 days ago
Penetration Tester / Red team Specialist

Raiffeisen Bank International AG
Stans, Austria
€47k
Linux
OAuth
Scripting
about 2 months ago
Staff Developer Advocate, GitHub Security Lab
GitHub
United States
Experienced
$121k–323k
Remote
Git
Github
Databases
about 2 months ago
Staff Hardware Security Engineer
Arm
München, Germany
€131k
U-Boot
Firmware
System on a…
about 2 months ago
Senior Threat Intelligence Analyst
ZEISS Group
Jena, Germany
Expert
Profiling
Cybercrime
Mitre Att&ck
about 2 months ago
Senior Cybersecurity Incident Responder
ZEISS Group
Jena, Germany
Expert
Mitre Att&ck
Cyber Warfare
Cyber Security