WeAreDevelopers LIVE Apr 29, 2022

Walking into the era of Supply Chain Risks

Vandana Verma

With 90% of your codebase built on open-source, who truly controls your software? Uncover how to defend your development pipeline against devastating supply chain attacks using zero-trust architecture.

Pause
Mute Enter Fullscreen
#1 about 2 min

Entering the era of software supply chain risks

How connected smart home devices create hidden vulnerabilities and dangerous privacy risks.

#2 about 2 min

Distributing malware through compromised developer tooling

Malicious actors exploit open-source maintainer fatigue by injecting crypto miners and loops into popular event-stream packages.

#3 about 2 min

Identifying risks in untracked open source software dependencies

The reliance on external dependencies introduces untracked vulnerabilities during urgent software release cycles.

#4 about 1 min

Targeting developer integrated development environments and plugins

Attackers increasingly compromise third-party IDE extensions to access source code repositories and intercept development workflows.

#5 about 2 min

The delayed resolution of vulnerabilities in open source

Maintainer constraints often lead to significant delays in patching known bugs like persistent cross-site scripting flaws.

#6 about 1 min

Responding effectively to exploits after security patch releases

The Equifax breach demonstrates the critical need to detect and respond rapidly when public exploits target known software vulnerabilities.

#7 about 3 min

Rapid delivery cycles expanding the software attack surface

Moving from yearly releases to instant deployments exposes continuous integration infrastructure to cascading infiltration.

#8 about 3 min

Examining common exploitation techniques against software organizations

Attackers utilize techniques like dependency confusion and build-time compromise to target consumer data through widespread software tooling.

#9 about 2 min

Implementing zero trust architectures for secure developer ecosystems

Replacing implicit trust with rigorous validation points creates stronger boundaries against infiltrated deployment environments.

#10 about 3 min

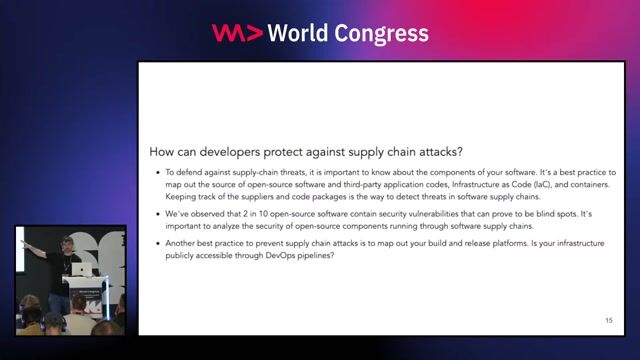
Adopting actionable frameworks for software bills of materials

Leveraging best practices from OpenSSF and CNCF helps teams secure hardware systems, source code, and deployment pipelines.

#11 about 3 min

Evaluating the global organizational impact of widespread vulnerabilities

The enduring threat of the Log4j Java framework exploit underscores the danger of pervasive remote code execution bugs.

#12 about 4 min

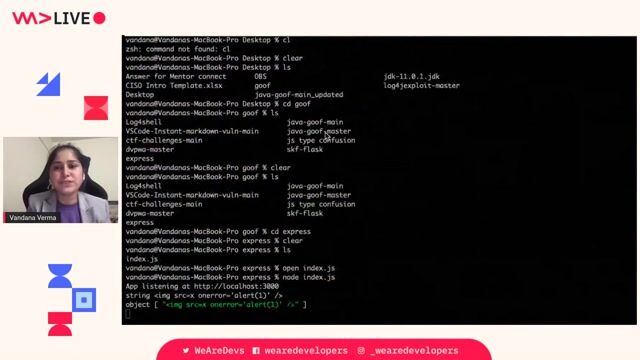
Demonstrating prototype pollution in input sanitization workflows

Bypassing string-based validation by injecting array objects highlights implicit trust failures in raw input handling.

#13 about 4 min

Reproducing remote code execution via log4shell ldap servers

Connecting a vulnerable Java instance to a malicious LDAP payload highlights how automated ransomware downloads infect systems.

#14 about 3 min

Exploiting python celery dependencies for internal container access

A proof-of-concept demonstrates how vulnerable background job workers can leak sensitive host variables and infrastructure identities.

#15 about 2 min

Creating secure baselines by tracking container environment configurations

Empowering software engineering teams with precise inventory visibility reduces the cognitive load during incident response.

#16 about 6 min

Bridging the gap between software development and security

Participating in cyber security meetups and executing Python script automation help professionals transition into security advocacy.

#17 about 4 min

Mitigating social engineering and identifying technical security resources

Expanding threat awareness requires prioritizing social vectors alongside configuration management and seeking guidance from experienced creators.

Matching moments

3:36 min

Understanding software supply chain threats and security risks

Andrei Epure Andrei Epure · World Congress 2024

2:46 min

Mapping the complete software supply chain attack surface

Matthew Brady Matthew Brady · World Congress 2026 Europe

3:39 min

Exploring the mechanics of software supply chain attacks

Chris Heilmann +2 · LIVE

2:00 min

Mitigating risks from supply chain attacks and vulnerable libraries

Jasmin Azemović Jasmin Azemović · World Congress 2023

3:09 min

Practical mitigation strategies for modern software supply chains

Adrian Mouat Adrian Mouat · World Congress 2026 Europe

2:10 min

Balancing rapid software updates against supply chain attack risks

Christian Heilmann Christian Heilmann +3 · World Congress 2026 Europe

Upcoming sessions on this topic

Open session

World Congress 2026 North America

September 23, 2026 · 14:00–14:30

Stage 1

Supply Chain Security When Agents Write the Code

Ajeet Raina

Developer Advocate, Docker

Ajeet Raina
Open session

World Congress 2026 North America

September 25, 2026 · 09:40–10:10

Stage 4

How Docker caught a supply chain attack in 83 minutes

Khushboo Verma

Systems Engineer at Cloudflare
Khushboo Verma
Open session

World Congress 2026 North America

September 25, 2026 · 13:30–14:00

Stage 9

On the Public Clock: Open-Source Defense When You're Not in the Club

Nicholas Muy

VP Engineering Platform and Security at Scrut.io

Nicholas Muy
Open session

World Congress 2026 North America

September 24, 2026 · 11:40–12:10

Stage 3

Stop Running Mystery Meat in Production

Jeroen van Erp

Technical Advocate @ SUSE

Jeroen van Erp
Open session

World Congress 2026 North America

September 24, 2026 · 12:15–12:45

Stage 6

AI vs. AI: Defending the open source supply chain with agentic workflows

Manfred Moser

Senior Principal DevRel Engineer at Chainguard
Manfred Moser
Open session

World Congress 2026 North America

September 23, 2026 · 15:45–17:45

Stage 10

Securing the Agentic Stack: Docker Hardened Images and Supply Chain Security

Ajeet Raina

Developer Advocate at Docker
Ajeet Raina