World Congress 2023 • Sep 27, 2023

Going Beyond Passwords: The Future of User Authentication

Gift Egwuenu

Are text-based passwords putting your application at risk? Learn to architect frictionless, phishing-resistant authentication using device-bound passkeys, WebAuthn, and single sign-on frameworks.

Pause
Mute Enter Fullscreen
#1 about 4 min

Introduction to modern authentication and web password vulnerabilities

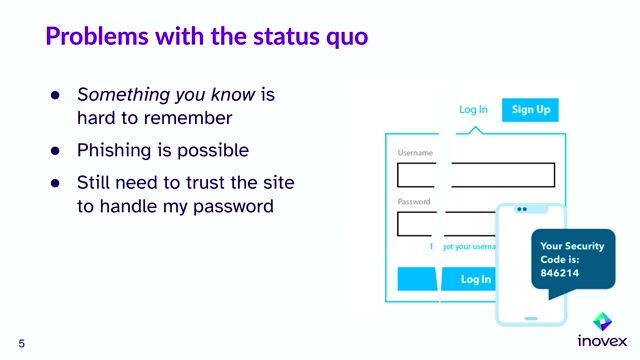
Traditional username and password combinations represent the primary vulnerability for modern web application data breaches.

#2 about 2 min

Implementing guidelines for strong and secure web passwords

Developers must enforce specific constraints like mixed capitalization, symbols, and length boundaries on login forms.

#3 about 3 min

Checking data breaches and utilizing centralized password managers

Verifying credentials against known data breaches combined with password managers centralizes general access safety.

#4 about 2 min

The risks of relying solely on public-private key passphrases

Misplacing hardcoded recovery phrases completely and permanently eliminates a user's ability to access secured accounts.

#5 about 4 min

Integrating passwordless authentication with magic links and SMS

Implementing one-time codes and magic links via the Auth0 Next.js SDK establishes secure passwordless environments.

#6 about 4 min

Layering security mechanisms with multi-factor authentication factors

Combining knowledge, possession, and biometrics through automated calls or authenticator applications ensures robust multilayered security.

#7 about 2 min

Securing application access with WebAuthn and physical FIDO keys

Physical FIDO keys mitigate severe phishing attacks by mandating specific hardware proximity for cross-browser sessions.

#8 about 3 min

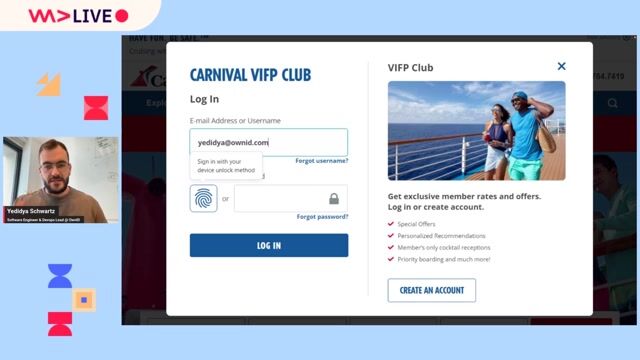
Replacing traditional website logins with biometric web passkeys

Linking user profiles directly to native device biometrics streamlines an entirely password-free web authentication cycle.

#9 about 5 min

Architecting single sign-on flows across multiple application domains

Routing authentication through central identity providers utilizes OIDC or SAML protocols to bypass same-origin strictness.

#10 about 2 min

Adopting modern authentication strategies within software development teams

Software teams should conduct deliberate security assessments to iteratively transition platform infrastructure away from conventional passwords.

#11 about 3 min

Addressing security risks with central single sign-on setups

Implementing enterprise-grade infrastructure utilizing account recovery protocols mitigates centralized vulnerabilities when mobile devices get lost.

Matching moments

1:53 min

Overcoming barriers to passwordless authentication adoption

Christoph Menzel Christoph Menzel · World Congress 2026 Europe

2:16 min

Analyzing friction in traditional authentication flows

Rahat Chowdhury · JS Congress

4:32 min

Shifting organizational security toward phishing-resistant authentication standards

Christoph Menzel Christoph Menzel · World Congress 2026 Europe

3:22 min

Accelerating adoption through developer resources and user education

Clemens Hübner Clemens Hübner · World Congress 2023

3:49 min

Navigating authentication challenges and third-party password managers

Christian Heilmann Christian Heilmann +1 · World Congress 2026 North America

4:13 min

Hardware keys and mitigating persistent password vulnerabilities

Chris Heilmann Chris Heilmann +2 · LIVE

Upcoming sessions on this topic

Open session

Shipping MCP to Real Users: Scaling, Auth, and the PII Leak You Didn't See Coming

  • Hadar Geva

    Myop

    CTO & Co-founder

Open session

Supply Chain Security for the Everyday Engineer

  • Pradumna Saraf

    Kestra Technologies

    Quality Assurance Engineer

Open session

Beware of Strangers Bearing Code: Open Source Trust in the Agent Era

  • Vikram Vaswani

    Consultant

Open session

How Google built a Consistent, Global Authorization System with Zanzibar (and you can too!)

  • Sohan Maheshwar

    AuthZed

    Lead Developer Advocate

Open session

Designing for Every Direction: Logical CSS for Global, Adaptive, and Effortlessly Reversible UIs

  • Vidhya Krishnamoorthy

    Morgan Stanley

    VP, Software Engineering Manager

Open session

Multi-Cloud Isn't a Project. It's a Side Effect.

  • Antonio Mendoza Pérez

    Temporal Technologies

    Staff Developer Success Engineer

  • Gaurav Thadani

    Temporal

    Staff Developer Success Engineer