WeAreDevelopers LIVE • May 8, 2024

Cracking the Code: Decoding Anti-Bot Systems!

Fabien Vauchelles

Why do enterprise scrapers fail despite using proxies? Learn to decode layered browser fingerprinting and bypass advanced anti-bot systems to scale your data collection.

Pause
Mute Enter Fullscreen
#1 about 2 min

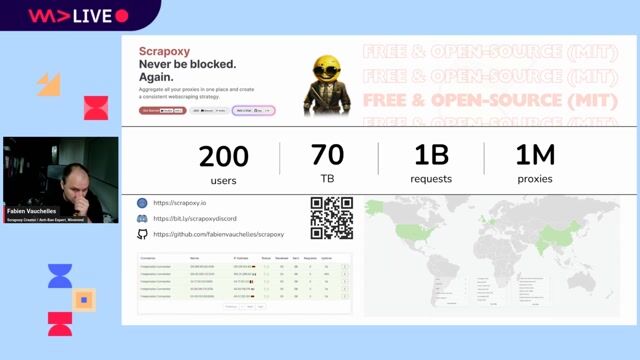
Introduction to web scraping and proxy aggregators

How continuous handling of airline prices led to full-time web scraping and the creation of an open-source proxy aggregator.

#2 about 3 min

Scaling data collection with automated virtual machines

Why straightforward web scraping leads to instant blocking without dynamic virtual machines to rotate server IPs.

#3 about 2 min

Organic interactions versus automated scraping behaviors

How analytical systems interpret connection actions as an automated Turing test to classify traffic intent.

#4 about 2 min

Detecting inconsistencies at the IP address layer

Investigating connection origins and metadata mismatching easily flags an attempt coming from non-residential centers.

#5 about 4 min

Fingerprinting TCP, TLS, and HTTP/2 protocol headers

Analyzing deep network packet flags enables deductions regarding specific client libraries attempting connections.

#6 about 2 min

Identifying bots through mandatory HTTP header order

Staring missing or out-of-order protocol headers immediately signals non-browser traffic logic to validation modules.

#7 about 2 min

Extracting granular hardware details via JavaScript execution

Browser script execution lets remote platforms capture detailed component analytics identifying exact rendering capacities.

#8 about 3 min

Tracking behavioral patterns and session reputation scores

Measuring raw event delays and movement curves generates sequential session classifications reflecting total automated reputation.

#9 about 3 min

Balancing false positives and limiting protection signals

Limiting signal tracking logic decreases rigid detection barriers in order to avoid locking legitimate customers away.

#10 about 2 min

Identifying targeted anti-bot signals using interceptors

Isolating defense requirements works best with application interceptors monitoring compiled code logic during payload generation.

#11 about 2 min

Architecture diagrams of modern automated browser defenses

Commercial platform gateways validate cookies mapped with secure reputation metrics fetched from external monitoring URLs.

#12 about 2 min

Securing analytical payloads using asymmetric cryptographic methods

Packaging captured client configurations with specialized public keys restricts manipulation when bypassing browser protections.

#13 about 4 min

Adapting scraping tools using headless browser setups

Wrapping automation instructions inside managed environments correctly populates complex header expectations previously blocked.

#14 about 4 min

Utilizing advanced rotating proxies and CAPTCHA solvers

Integrating external residential or mobile devices effectively solves strict rate constraints implemented at data centers.

#15 about 3 min

Structuring scalable infrastructure layers for robust extraction

Separating request tasks into central databases properly synchronizes vast execution farms avoiding duplication traps.

#16 about 3 min

Bypassing advanced payload generation and code obfuscation

Targeting high profile platforms requires breaking unreadable logic scripts generating specific hidden signal flags.

#17 about 3 min

De-obfuscating syntax with string modifying transformation trees

Unfolding split constants uncovers readable application variables allowing manual translation of secure encoded mechanisms.

#18 about 3 min

Defeating control flow confusions and state machines

Removing intentionally misleading code branches simplifies abstract machine operations slowing traditional debugging traces.

#19 about 3 min

Analyzing automated detection tags and rendering fingerprints

Resolving integrity checksums forces the emulator settings to precisely mimic native hardware rendering attributes.

#20 about 2 min

Future anti-bot directions using proprietary JavaScript virtual machines

Translating logic into closed environment bytecodes replaces traditional obfuscation making source regeneration effectively impossible.

#21 about 2 min

Limitations of commercial VPN setups during rotation

Relying strictly on generic tunneling limits massive requests since known VPN routing gets instantly blacklisted.

#22 about 3 min

Navigating legality frameworks regarding distributed bandwidth attacks

Avoiding personal data harvesting and mitigating network overload prevents automated collection operations from becoming destructive problems.

#23 about 2 min

Recognizing structural bot invasions using commercial protection

Applying analytical scoring models efficiently screens aggressive remote extraction software from draining operational server capacity.

#24 about 2 min

Building required skills for anti-bot framework creation

Combining foundational networking layers with script reversing abilities ensures engineers construct impenetrable monitoring operations.

#25 about 2 min

Updating defensive algorithms to match emerging attacks

Adapting monitoring techniques creates a constant cycle of requirement deployments between scrapers and defensive teams.

#26 about 2 min

Calculating successful proxy ratios against rate limits

Tracking extraction failures correctly dictates required request volume thresholds maintaining smooth remote server data handling.

#27 about 3 min

Contrast of API scraping variations against web traffic

Intercepting mobile endpoint responses accesses specific operating parameters requiring different replication procedures than raw desktop browsers.

Matching moments

3:40 min

Overcoming modern anti-bot mechanisms and network access restrictions

Vidas Bacevičius Vidas Bacevičius · World Congress 2025

5:54 min

The technical evolution of modern web scraping infrastructure

Chris Heilmann Chris Heilmann +4 · LIVE

2:20 min

Handling http network errors and anti-scraping challenges

Domagoj Marić Domagoj Marić · Europe 2026 Virtual

2:01 min

Bypassing anti-bot protections with proxies and emulation

Jan Curn Jan Curn · World Congress 2025

2:14 min

Understanding the basic mechanics of automated web scraping

Vidas Bacevičius Vidas Bacevičius · World Congress 2025

3:43 min

Scaling web scraping infrastructure to bypass strict security restrictions

Tim Ruscica · Coffee With Developers