

LM
Luis Minvielle
9 Ways to Make Money Hacking
over 2 years ago
Cyber Threat Hunter At ING Hubs Spain we are looking for aCyber Threat Hunter .Your role and work environment are driven by curiosity and the motivation to stay ahead of cyber adversaries.As a Cyber Threat Hunter, you will proactively uncover advanced and hidden threats before they become incidents, think like an attacker, challenge assumptions, and help strengthen ING’s resilience against evolving cyber risks.Team You will join ING’sGlobal Threat Management (GTM)team, a central capability within the CISO domain that focuses on intelligence-driven, proactive defense.The team works across geographies and disciplines to anticipate emerging threats, investigate advanced attack scenarios, and continuously improve ING’s detection and defensive posture.Collaboration, communication, ownership and impact are core to how we work.Key ResponsibilitiesProactively conductintelligence-led threat huntingbased on emerging threats, adversary activity, and major external cyber incidents.Develop and testhypothesis-driven investigationsto identify unknown or evasive malicious activity.Analyze adversary behaviour across thefull attack chain , identifying detection and control gaps.Translate hunt outcomes intoactionable improvementsfor detection, prevention, and defensive architecture.Map findings toMITRE ATT&CKto clearly articulate threats, gaps, and priorities.Communicate investigation outcomes inclear, executive-ready reportsthat support risk-based decision making.Leverageautomation, AI-assisted analytics, and Breach & Attack Simulation (BAS)to continuously validate threat hypotheses, test adversary techniques and prioritize high-risk attack paths.QualificationsSeveral years of hands-on experience in threat hunting activities.Ability to translate threat intelligence into concrete, high-impact investigations.Skill in identifying meaningful security gaps rather than chasing alerts or noise.Capacity to think and reason like an adversary while acting as a defender.Ability to deliver investigation outcomes that improve detection, controls or resilience.Clear communication of complex threats to both technical and non-technical stakeholders.Ability to work effectively in an environment with ambiguity, autonomy and high trust.Extra PointsExperience or relevant certifications in cyber threat hunting, detection engineering or adversary simulation (e.g., GIAC, MITRE ATT&CK, cloud security or BAS-related certifications) are considered an advantage.Benefits Flexible remuneration model with benefits such as nursery, transport card, training aids…Transport allowance to help you get to the office.Pension plan available after one month of employment.Health insurance for you and your family (spouse/partner and children).Life insurance to protect what matters most.Restaurant card to cover lunch expenses.Electric mobility solutions, doctor, hairdresser, gym and The Good Service to help you with errands available in our offices.Flexible work model allowing you to decide which days you work at home and which you come to ING MAD.#J-*****-Ljbffr
Several years of hands-on experience in threat hunting activities. Ability to translate threat intelligence into concrete, high-impact investigations. Skill in identifying meaningful security gaps rather than chasing alerts or noise. Capacity to think and reason like an adversary while acting as a defender. Ability to deliver investigation outcomes that improve detection, controls or resilience. Clear communication of complex threats to both technical and non-technical stakeholders. Ability to work effectively in an environment with ambiguity, autonomy and high trust. Extra Points Experience or relevant certifications in cyber threat hunting, detection engineering or adversary simulation (e.g., GIAC, MITRE ATT&CK, cloud security or BAS-related certifications) are considered an advantage.
Benefits Flexible remuneration model with benefits such as nursery, transport card, training aids… Transport allowance to help you get to the office. Pension plan available after one month of employment. Health insurance for you and your family (spouse/partner and children). Life insurance to protect what matters most. Restaurant card to cover lunch expenses. Electric mobility solutions, doctor, hairdresser, gym and The Good Service to help you with errands available in our offices. Flexible work model allowing you to decide which days you work at home and which you come to ING MAD. #J-*****-Ljbffr
This job is hosted externally. Click below to view the full posting and apply.
Talks and stories from around this role — technically off-topic, practically not.
3:29 min
1:38 min
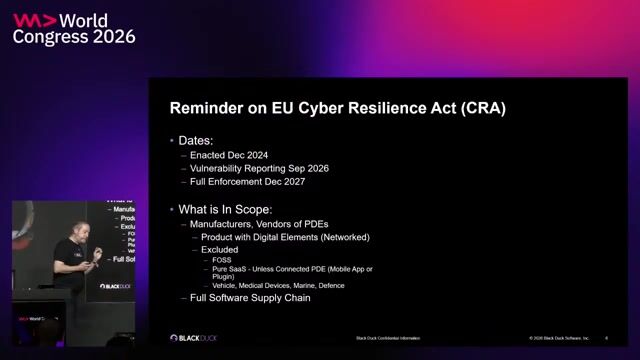
 Julian Totzek-Hallhuber · World Congress 2026 Europe
3:46 min
1:31 min
2:35 min
1:06 min