

BB
Benedikt Bischof
Open Source Secure Software Supply Chain in action
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
Software supply chain attacks are escalating. Protect your development lifecycle using open-source tools like Sigstore and Tekton. Watch a live demonstration of shifting your pipeline security left.
Matching moments
2:46 min
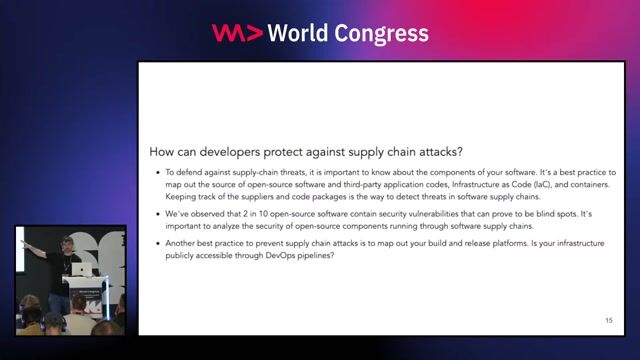
Mapping the complete software supply chain attack surface
 Matthew Brady · World Congress 2026 Europe
3:36 min
Understanding software supply chain threats and security risks
 Andrei Epure · World Congress 2024
1:37 min
Introduction to supply chain security principles
Zbyszek Tenerowicz · LIVE
4:00 min
Core principles for implementing DevSecOps in teams
Aarno Aukia · LIVE
2:35 min
Integrating security across the application development lifecycle
 Niels Tanis · World Congress 2022
3:39 min
Exploring the mechanics of software supply chain attacks
 Chris Heilmann +2 · LIVE
More from World Congress 2024
Related videos
Related articles

AB
Andre Braun, GitLab

DC
Daniel Cranney

CH
Chris Heilmann
From learning to earning
Jobs that call for the skills explored in this talk.
about 1 month ago
•
Verified
Senior Supply Chain Security Engineer
Docker, Inc.
Expert
Remote
Linux
Kubernetes
about 1 month ago
•
Verified
Senior Principal Software Engineer, Docker and Ecosystem
Docker, Inc.
Seattle, United States
Expert
Remote
Cloud (AWS/Google/Azure)
about 1 month ago
•
Verified
Senior Software Engineer, Secure Build
Docker, Inc.
Expert
Remote
Go
about 1 month ago
•
Verified
Principal Software Engineer, Docker Hardened Images
Docker, Inc.
Expert
Remote
Kubernetes
about 1 month ago
•
Verified
Manager, Engineering, Secure Build and SCS Services
Docker, Inc.
Expert
Remote
Team Leadership
about 1 month ago
•
Verified
Senior Security Engineer, Docker Desktop
Docker, Inc.
Expert
Remote
Go