
CH
Chris Heilmann
How GitHub secures open source
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
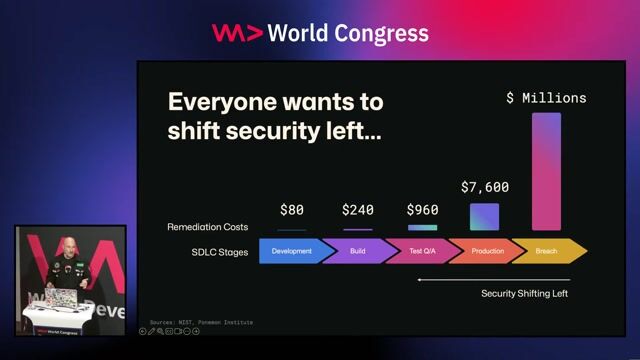
Cybersecurity suffers from a fixing problem, not a detection problem. Discover how GitHub leverages AI to help developers resolve vulnerabilities directly inside pull requests before reaching production.
Matching moments
2:45 min
Sourcing vulnerabilities and encouraging open source collaboration
Anna Oliveira · Coffee With Developers
2:39 min
Collaborating on secure coding environments and open sourcing solutions
1:34 min
Navigating security risks in AI-assisted open source contributions
 Cédric Gégout +4 · World Congress 2026 Europe
1:29 min
Assisting security analysis using AI code review tools
 Matteo Meucci · Europe 2026 Virtual
1:59 min
Navigating the impact of AI on open source maintenance
 Sinduri Guntupalli · World Congress 2026 Europe
2:18 min
Handling the surge of AI-generated open-source code contributions
 Michele Zuccala +4 · World Congress 2026 Europe
More from World Congress 2025
Related videos
Related articles
CH
Chris Heilmann
CH
Chris Heilmann

BB
Benedikt Bischof

From learning to earning
Jobs that call for the skills explored in this talk.
about 2 months ago
Staff Developer Advocate, GitHub Security Lab
GitHub
United States
Experienced
$121k–323k
Remote
Git
Github
Databases
13 days ago
Senior Software Engineer
GitHub
United States
Expert
$124k–329k
Remote
Ruby
Golang
DevOps
about 1 month ago
Staff Software Engineer, GitHub Intelligence (Copilot Agents)
GitHub
San Francisco, CA, United States
Experienced
Ruby
Golang
Github
29 days ago
•
Verified
Senior Supply Chain Security Engineer
Docker, Inc.
Expert
Remote
Linux
Kubernetes
about 1 month ago
•
Verified
Founding Developer Advocate
Plumber
San Francisco, United States
Experienced
$150k–190k
Remote
GIT
Bash
Linux
3 months ago
Senior Software Engineer, Enterprise Products
GitHub
United States
Expert
$124k–329k
Remote
Ruby
Bicep
Golang