WeAreDevelopers LIVE • Feb 12, 2024

Securing secrets in the GitOps Era

Davide Imola

Storing plain-text Kubernetes secrets in Git exposes your entire infrastructure. How can you protect sensitive credentials without breaking automated deployment pipelines driven by Flux or ArgoCD?

Pause
Mute Enter Fullscreen
#1 about 6 min

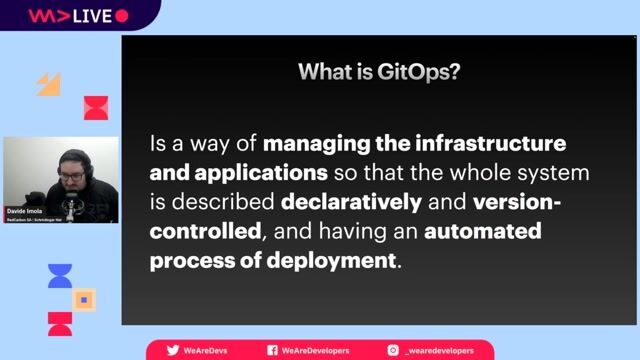
Understanding principles and benefits of the GitOps workflow

How declarative version control establishes a unified deployment path for clusters.

#2 about 5 min

Security risks of storing native Kubernetes secrets in git

Why relying on standard base64 encoding exposes sensitive passwords within version control.

#3 about 4 min

Encrypting configurations with the Sealed Secrets cluster operator

Utilizing asymmetric keys to securely store and decrypt configuration data inside clusters.

#4 about 13 min

Demonstration of kubeseal encryption and Flux deployment reconciliation

A practical walkthrough encrypting manual credentials and verifying automated cluster deployment reconciliation.

#5 about 4 min

Evaluating the operational trade-offs of Sealed Secrets

The simplicity of native configurations compared to the manual overhead of updating payloads.

#6 about 5 min

Advanced credential rotation utilizing dedicated Secrets Managers

Deploying centralized database platforms enables granular management interfaces and automated credential scaling.

#7 about 5 min

Integrating cluster resources directly with Secrets Managers

Connecting cluster workloads securely utilizing dedicated provider libraries and container storage interfaces.

#8 about 19 min

Audience Q&A on tenant isolation and continuous integration

Strategies for isolating access layers, restricting public interfaces, and adapting permissions dynamically.

Matching moments

6:14 min

Introduction to securing secrets in GitOps deployments

Alex Soto Alex Soto · LIVE

3:42 min

Managing secrets and security in a GitOps model

Roberth Strand · LIVE

2:03 min

Additional resources on GitOps and Kubernetes secret management

Alex Soto Alex Soto · LIVE

3:09 min

Injecting sensitive configuration values via Kubernetes secrets

Hannes Norbert Göring · LIVE

2:30 min

Handling passwords and certificates securely via Kubernetes secrets

Aurélie Vache Aurélie Vache · World Congress 2026 Europe

4:29 min

Configuring a DevSecOps pipeline and Oversecured integration demo

Moataz Nabil Moataz Nabil · LIVE

Upcoming sessions on this topic

Open session

Supply Chain Security for the Everyday Engineer

  • Pradumna Saraf

    Kestra Technologies

    Quality Assurance Engineer

Open session

We Deleted Our Observability Stack and Rebuilt It with OTEL: 12 Engineers to 4 at 20K+ clusters

  • Yash Sharma

    DigitalOcean

    Developer Advocate

Open session

Beware of Strangers Bearing Code: Open Source Trust in the Agent Era

  • Vikram Vaswani

    Consultant

Open session

Architecting Trusted AI: Coupling Multi-Agent Systems with dbt Semantic Store for Zero-Hallucination

  • Pushkar Mishra

    J.P. Morgan

    Senior Vice President

Open session

How We Cut Our API's p99 Latency from Minutes to Under a Second

  • Deepak Agrawal

    Atlassian

    Principal Software Engineer

Open session

Beyond File Dumps: Context Engineering for Coding Agents

  • Animesh Dutta

    Arm

    Senior Software Engineer