World Congress 2024 • Aug 20, 2024 • Session details

Cross Site Scripting is yesterday's news, isn't it?

martinakraus

Think modern frameworks cured XSS? They haven't. Learn how to lock down your application against native DOM bypasses using strict CSPs and Trusted Types.
Cross Site Scripting is yesterday's news, isn't it? thumbnail

Checking access…

Playback and chapters load privately for Free videos.

Matching moments

1:05 min

Handling modern injection flaws and cross-site scripting

Christian Wenz Christian Wenz · World Congress 2026 Europe

1:35 min

Enhancing core browser security with the native HTML Sanitizer API

Chris Heilmann Chris Heilmann +2 · LIVE

1:44 min

Evaluating framework architectures against cross-site scripting attack vectors

Philippe De Ryck · LIVE

4:58 min

Dealing with cross-site scripting in single page applications

Thomas Konrad · LIVE

1:43 min

Stopping cross-site scripting attacks via secure HTML types

Michael Koppmann · LIVE

2:07 min

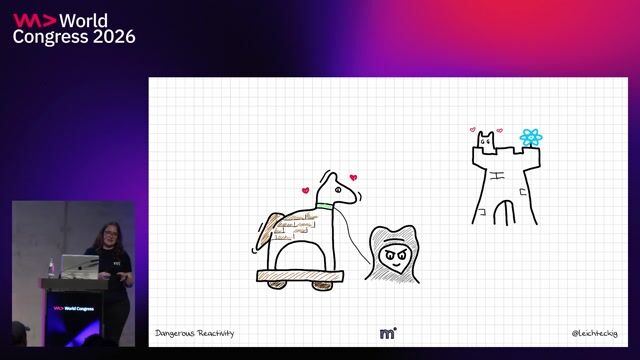
Understanding classic XSS risks in reactive frontend frameworks

Ramona Schwering Ramona Schwering · World Congress 2026 Europe

Upcoming sessions on this topic

Open session

Supply Chain Security for the Everyday Engineer

  • Pradumna Saraf

    Kestra Technologies

    Quality Assurance Engineer

Open session

Your Server-Rendered App Doesn't Know Who It's Talking To

  • Anshul Bansal

    OLX India

    Principal Architect

Open session

When Caches Lie: Solving Transactional Integrity and Distributed Race Conditions in Spring Boot

  • Shuchita Prasad

    JPMorgan

    Senior Lead Engineer

Open session

Understanding React Performance Patterns Developers Often Get Wrong

  • Himanshu Srivastava

    Best Buy India

    Software Engineer

Open session

Beware of Strangers Bearing Code: Open Source Trust in the Agent Era

  • Vikram Vaswani

    Consultant

Open session

The UI Engineering Playbook: Modern CSS, Design Systems, Motion & AI-Assisted Workflows

  • Wadad Parker

    Ednius Inc.

    SDE