World Congress 2025 • Aug 20, 2025 • Session details

Friend or Foe? TypeScript Security Fallacies

Liran Tal

Are your TypeScript interfaces leaving your Node.js backend exposed? Discover how attackers bypass static compile-time checks and learn to implement strict runtime validation.

Pause
Mute Enter Fullscreen
#1 about 3 min

Context of npm vulnerabilities and TypeScript security assumptions

Introducing the false assumption that TypeScript provides embedded security guardrails during backend development.

#2 about 5 min

Analyzing HTTP parameter pollution and unexpected backend behaviors

How passing multiple types of parameters in HTTP requests creates unexpected and potentially vulnerable backend behavior.

#3 about 6 min

Bypassing type constraints using type juggling and array inputs

Why forcing type casting or relying on standard interfaces fails to protect against array-based type juggling.

#4 about 3 min

Understanding the limitations of compile-time TypeScript safety checks

Why development-time type checking must be combined with runtime techniques like type narrowing to prevent vulnerabilities.

#5 about 7 min

Exploiting Zod schema validation through prototype pollution attacks

How malicious actors inject prototype values to bypass runtime schemas and manipulate object inheritance in JavaScript.

#6 about 3 min

Bypassing database ORM safety mechanisms via unvalidated mass assignments

Why loosely parsed runtime schemas allow privilege escalation when passing objects directly into object-relational mappers.

#7 about 3 min

Analyzing real-world structural vulnerabilities in popular npm dependency packages

Reviewing actual vulnerability disclosures in popular open-source libraries caused by unhandled type variations and prototype pollution.

#8 about 2 min

Rethinking application design and standard code type safety practices

Why software engineering teams must treat type definitions like code coverage instead of robust security protections.

Matching moments

2:00 min

The origins and early problems solved by TypeScript

Dani Coll Dani Coll · World Congress 2026 Europe

2:28 min

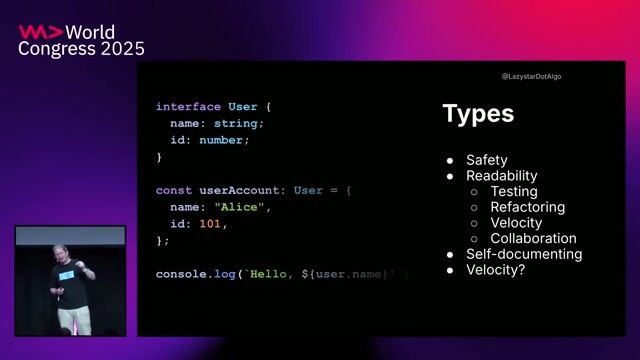
Exploring the benefits of type safety and TypeScript migration

Chris Heilmann +2 · LIVE

1:00 min

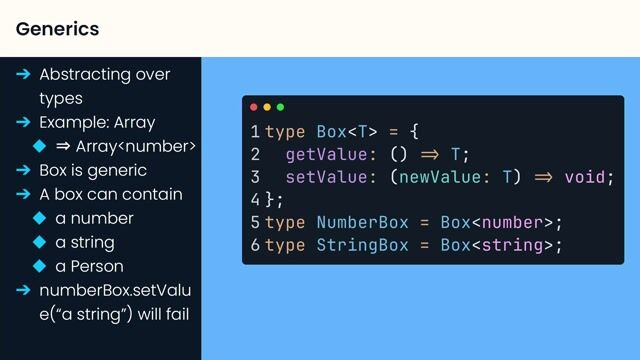
Misconceptions about TypeScript safety capabilities

Simone Sanfratello · JS Congress

4:58 min

Introduction to hidden problems in typical TypeScript code

Stefan Baumgartner · World Congress 2023

4:34 min

Discovering the hidden drawbacks of advanced type mitigations

Stefan Baumgartner · World Congress 2023

3:08 min

Introduction to basic TypeScript capabilities and type annotations

Jens Claes · World Congress 2023

Upcoming sessions on this topic

Open session

World Congress 2026 North America

September 25, 2026 · 16:15–16:25

Outdoor Stage

Silent Execution: Defending Against Install-Time Supply Chain Attacks

Chris DeMars

Senior Developer Advocate at TuxCare
Chris DeMars
Open session

World Congress 2026 North America

September 24, 2026 · 14:50–15:20

Stage 1

The Era of Machine-Driven Defense is Here: Headless Security

Loris Degioanni

Founder & CTO of Sysdig
Loris Degioanni
Open session

World Congress 2026 North America

September 24, 2026 · 14:10–14:40

Stage 2

Know Your Enemies: Live Exploit of a PHP Engine Security Breach

Alexandre Daubois

CTO of Les-Tilleuls.coop / Symfony Core Team / PHP & FrankenPHP Core Maintainer

Alexandre Daubois
Open session

World Congress 2026 North America

September 25, 2026 · 14:50–15:20

Outdoor Stage

On the Public Clock: Open-Source Defense When You're Not in the Club

Nicholas Muy

VP Engineering Platform and Security at Scrut.io

Nicholas Muy
Open session

World Congress 2026 North America

September 24, 2026 · 11:40–12:10

Stage 3

Stop Running Mystery Meat in Production

Jeroen van Erp

Technology Advocate @ SUSE

Jeroen van Erp
Open session

World Congress 2026 North America

September 24, 2026 · 16:00–18:00

Stage 13

Practical Threat Modeling for Software Developers

Mudassir Syed

Lead Security Software Engineer

Mudassir Syed