
DC
Daniel Cranney
WeAreDevelopers LIVE
•
Feb 24, 2022
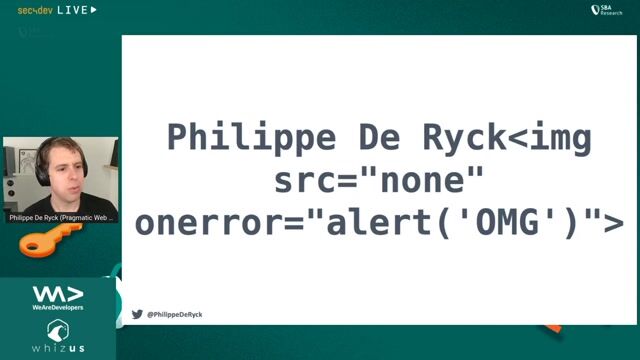
Securing Frontend Applications with Trusted Types
Philippe De Ryck
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
Stop trusting static analysis to catch elusive DOM-based XSS. Move protection directly to the browser with Trusted Types to neutralize risky bypasses and unpatched third-party vulnerabilities forever.
Matching moments
1:44 min
Enforcing safe HTML assignments using Trusted Types policies
 martinakraus · World Congress 2024
2:20 min
Enforcing strict DOM APIs using trusted types
Thomas Konrad · LIVE
1:35 min
Enhancing core browser security with the native HTML Sanitizer API
 Chris Heilmann +2 · LIVE
3:37 min
Generating Trusted Types safely using the DOMPurify library
martinakraus · World Congress 2024
1:43 min
Stopping cross-site scripting attacks via secure HTML types
Michael Koppmann · LIVE
3:07 min
Implementing zero trust security practices in frontend applications
 Jan Peer Stöcklmair · World Congress 2026 Europe
More from WeAreDevelopers LIVE
Related videos
Related articles

BB
Benedikt Bischof

CH
Chris Heilmann

DC
Daniel Cranney

From learning to earning
Jobs that call for the skills explored in this talk.
21 days ago
Senior Software Engineer, Angular
Bitpanda
Barcelona, Spain
Remote
Backend
Caching
ReactJS
24 days ago
Frontend Engineer

Almedia
Berlin, Germany
Expert
€80k–140k
NestJS
ReactJS
TypeScript
about 1 month ago
•
Verified
Founding Engineer (Front End)
Momentic
San Francisco, United States
Expert
$180k–220k
React
Next.js
JavaScript
5 days ago
Software Engineer, Angular (B2C Web Platform)
Bitpanda
Barcelona, Spain
Remote
ReactJS
Caching
AngularJS
about 2 months ago
Senior AI Frontend Engineer

TeamViewer Germany GmbH,
Austin, TX, United States
Expert
ReactJS
TypeScript
Material UI
about 1 month ago
•
Verified
Staff Frontend Software Engineer
Bitdrift
Expert
Remote
React
JavaScript
TypeScript