
DC
Daniel Cranney
WeAreDevelopers LIVE
•
Apr 27, 2023
This Machine Ends Data Breaches
Liz Moy
- Discuss this with your agent
- Open in Claude
- Open in ChatGPT
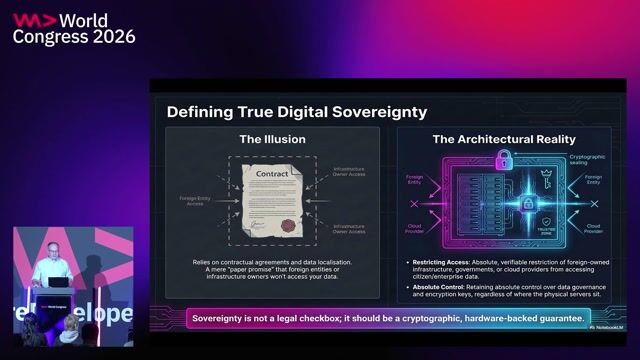
Your encrypted data is completely vulnerable the second it enters a CPU cache. Learn how Trusted Execution Environments cryptographically isolate active memory to definitively end runtime breaches.
Matching moments
5:02 min
Hardware isolation through privacy enhancing technologies
 Mingshen Sun · World Congress 2025
49 sec
Hardware-based trusted execution environments for confidential computing
 Rob Nertney · World Congress 2026 Europe
4:08 min
Securing data in use with confidential cloud computing
 Isha Salania · World Congress 2026 Europe
2:48 min
Utilizing trusted execution environments for data protection
Mingshen Sun · World Congress 2026 Europe
2:44 min
Advancing confidential computing with open source multi-way collaboration
Mingshen Sun · World Congress 2024
5:17 min
Addressing availability, latency overheads, and hardware trust concerns
 Mike Bursell · World Congress 2026 Europe
More from WeAreDevelopers LIVE
Related videos
Related articles

AH
Aishi Huang
CH
Chris Heilmann
CH
Chris Heilmann

DC
Daniel Cranney

From learning to earning
Jobs that call for the skills explored in this talk.
21 days ago
Principal Software Engineer, AI Compute Infrastructure

ARM
Seattle, WA, United States
Expert
$262k
Linux
Grafana
Pytorch
28 days ago
•
Verified
SoC Offensive Security Staff Engineer
Arm
Austin, United States
Experienced
$198k–268k
Remote
Network Security
about 1 month ago
•
Verified
ML Engineer
Docker, Inc.
Seattle, United States
Expert
Remote
Go
21 days ago
Principal Software Engineer, AI Inference Runtime
ARM
Seattle, WA, United States
Expert
$262k
Compilers
Low Latency
Concurrency
17 days ago
Security Engineer - Product - Remote

Qdrant
Madrid, Spain
Remote
Pulumi
DevOps
Terraform
about 1 month ago
•
Verified
GPU Cluster Engineer, Systems & Platform
Sciforium
San Francisco, United States
Expert
$150k–220k
Kubernetes