World Congress 2025 • Aug 20, 2025 • Session details

Kubernetes Security Best Practices

Rico Komenda

Nine out of ten organizations suffer a Kubernetes security incident annually. Master the foundational defenses needed to lock down your clusters from individual containers to network traffic.

Pause
Mute Enter Fullscreen
#1 about 5 min

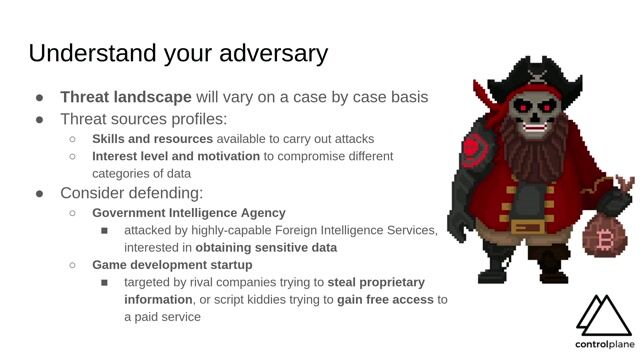
Assessing common Kubernetes security incidents and misconfigurations

Identifying common security incidents and persistent misconfigurations within modern platform architectures.

#2 about 2 min

Understanding the four Cs of cloud native security

Securing the entire infrastructure stack across cloud, cluster, container, and code layers.

#3 about 3 min

Securing container images in the build process

Preventing malicious breakouts by scanning artifacts and removing unnecessary dependencies during builds.

#4 about 4 min

Enforcing non-root execution and pod security standards

Restricting container privileges using dedicated user accounts and robust pod security admission profiles.

#5 about 3 min

Restricting cluster rights with role-based access controls

Mitigating unauthorized cluster actions by applying the principle of least privilege to service accounts.

#6 about 3 min

Isolating pod communication with strict network policies

Limiting internal pod traffic using explicit container network interface rules and service meshes.

#7 about 2 min

Protecting the ETCD cluster data store

Securing the critical cluster backing store against unauthorized access using dedicated TLS certificates.

#8 about 4 min

Automating security policies and admission controller takeaways

Enforcing declarative rules through admission controllers to sustainably harden overall infrastructure.

Matching moments

1:59 min

Implementing standard Kubernetes cluster security practices

Ali Alp Ali Alp · World Congress 2026 Europe

1:39 min

Introduction to Kubernetes security challenges and opportunities

Marc Nimmerrichter · World Congress 2022

1:19 min

Securing Kubernetes workloads and containerized image layers

Aleksandr Kalikov · LIVE

11:32 min

Audience questions on security, limitations, and Kubernetes crossover

Maurice Brinkmann · LIVE

3:43 min

Introduction to Kubernetes security context configurations

Dimitrij Klesev +1 · LIVE

2:28 min

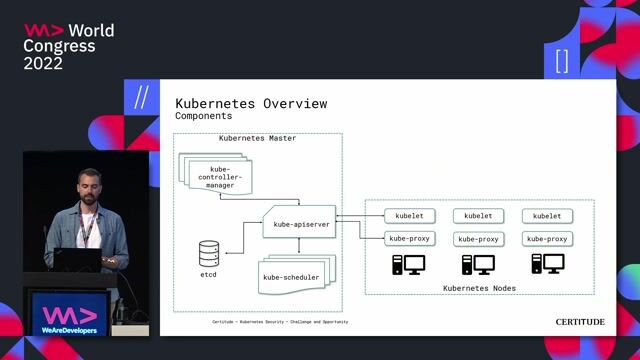
Understanding Kubernetes architecture and core cluster components

Marc Nimmerrichter · World Congress 2022

Upcoming sessions on this topic

Open session

World Congress 2026 North America

September 24, 2026 · 11:40–12:10

Stage 3

Stop Running Mystery Meat in Production

Jeroen van Erp

Technical Advocate @ SUSE

Jeroen van Erp
Open session

World Congress 2026 North America

September 23, 2026 · 15:45–17:45

Stage 10

Securing the Agentic Stack: Docker Hardened Images and Supply Chain Security

Ajeet Raina

Developer Advocate at Docker

Ajeet Raina
Open session

World Congress 2026 North America

September 25, 2026 · 09:40–10:10

Stage 4

Your registry can't stop a valid login. What happens then?

Khushboo Verma

Systems Engineer at Cloudflare
Khushboo Verma
Open session

World Congress 2026 North America

September 25, 2026 · 15:30–16:00

Mainstage

One Boundary for the Agentic Era

Mark Lechner

Chief Information Security Officer of Docker
Mark Lechner
Open session

World Congress 2026 North America

September 25, 2026 · 12:30–14:30

Stage 13

Docker sandboxes: protect your secrets, tokens, and personal data from AI agent mistakes

Kristiyan Velkov

Developer Relations Engineer at Zerops.io
Kristiyan Velkov
Open session

World Congress 2026 North America

September 25, 2026 · 10:20–10:50

Stage 4

rm -rf: Horror Stories From Unsandboxed AI Agents (and How Docker Fixes This)

Rishab Kumar

Staff Developer Evangelist @ Twilio

Rishab Kumar