World Congress 2026 Europe Jul 10, 2026 Session details

Diagnostic Tooling: How to get insights from your .NET services hosted in Kubernetes containers?

Tom Crecelius

Struggling to extract diagnostic data from hardened, shell-less Kubernetes containers? Learn how to securely generate memory dumps and CPU traces using dotnet-monitor as a decoupled sidecar.

Pause
Mute Enter Fullscreen
#1 about 4 min

Defining diagnostic artifacts and their continuous importance

Diagnostic artifacts like files and captured data help analyze runtime conditions for troubleshooting and optimization.

#2 about 2 min

Building blocks of the .NET diagnostic ecosystem

Events, event counters, and memory dumps form the technical foundation of .NET runtime analysis.

#3 about 3 min

Extracting runtime data with event pipes and diagnostic ports

Event pipes emit continuous data streams while diagnostic ports enable two-way communication between the runtime and external tools.

#4 about 2 min

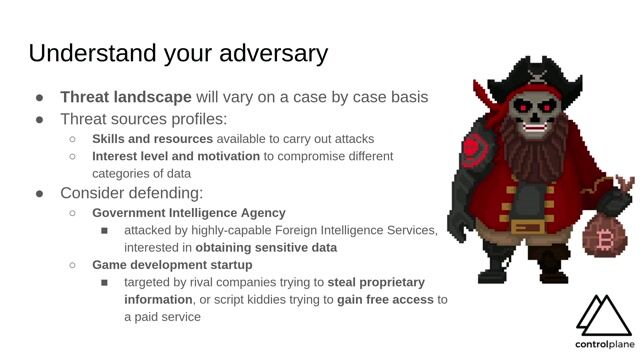
Challenges of diagnosing services in secured Kubernetes clusters

Hardened container images restrict standard analysis tools and limit the ability to execute inside pods.

#5 about 4 min

Security risks of baking diagnostic tools into application images

Including troubleshooting utilities inside production containers compromises security and violates the minimum-privilege principle.

#6 about 2 min

Centralizing artifact collection using dotnet monitor via APIs

The dotnet monitor tool enables on-demand trace creation and rule-based diagnostic triggers without compromising application boundaries.

#7 about 2 min

Configuring a diagnostic sidecar container in Kubernetes pods

A dedicated sidecar securely shares a diagnostic port volume with the main application for safe external investigation.

#8 about 3 min

Customizing diagnostic port locations for enhanced security

Using a dedicated diagnostic folder instead of the default temporary directory prevents unintentional access by other shared components.

#9 about 3 min

Securing the HTTP API with authentication and TLS encryption

Production deployments of dotnet monitor require secure API keys and TLS certificates mounted via Kubernetes secrets.

#10 about 2 min

Automating artifact storage using secure egress providers

Egress providers allow immediate and secure export of diagnostic artifacts to external locations like network shares or blob storage.

#11 about 5 min

Injecting ephemeral debug containers into running Kubernetes pods

Ephemeral containers offer a lightweight, temporary alternative to sidecars but require specialized APIs to enable necessary volume mounts.

#12 about 3 min

Summary of container diagnostics and garbage collector behavior

A brief recap of the recommended diagnostic approaches and clarification on how memory dumps automatically trigger garbage collection.

Matching moments

1:33 min

Debugging serverless container applications in Kubernetes production environments

Alex Soto Alex Soto · LIVE

1:39 min

Introduction to Kubernetes security challenges and opportunities

Marc Nimmerrichter · World Congress 2022

4:40 min

Assessing common Kubernetes security incidents and misconfigurations

Rico Komenda Rico Komenda · World Congress 2025

2:10 min

Optimizing software development for production and Kubernetes

Josh Long · World Congress 2022

3:01 min

Decomposing infrastructure problems using sandbox environments and networking tools

Ingvord Ingvord · World Congress 2024

4:31 min

Addressing local development challenges with Podman Desktop

Stevan Le Meur Stevan Le Meur · World Congress 2024

Upcoming sessions on this topic

Open session

World Congress 2026 North America

September 24, 2026 · 11:40–12:10

Stage 3

Stop Running Mystery Meat in Production

Jeroen van Erp

Technical Advocate @ SUSE

Jeroen van Erp
Open session

World Congress 2026 North America

September 25, 2026 · 09:00–09:30

Stage 1

Test Before Release, Enforce at Runtime: Governance for Tool-Using AI Agents

Sachin Gupta

Member of Technical Staff 2 at eBay

Sachin Gupta
Open session

World Congress 2026 North America

September 25, 2026 · 09:40–10:10

Stage 4

Your registry can't stop a valid login. What happens then?

Khushboo Verma

Systems Engineer at Cloudflare
Khushboo Verma
Open session

World Congress 2026 North America

September 25, 2026 · 12:30–14:30

Stage 13

Docker sandboxes: protect your secrets, tokens, and personal data from AI agent mistakes

Kristiyan Velkov

Developer Relations Engineer at Zerops.io
Kristiyan Velkov
Open session

World Congress 2026 North America

September 24, 2026 · 15:30–16:00

Stage 9

Run your agents in Kubernetes: Build once, deploy anywhere. But really?

Michal Salanci

Senior Systems Engineer at ESET Cybersecurity

Michal Salanci
Open session

World Congress 2026 North America

September 23, 2026 · 15:45–17:45

Stage 8

Docker's Agentic Platform: Sandboxes, MCP, and the Infrastructure of Autonomous Development

Oleg Šelajev

AI and Developer Relations at Docker
Oleg Šelajev